Which Groups Grant Least Privilege to Add a Windows Server 2022 DC?
Your network contains an Active Directory Domain Services (AD DS) forest. The forest functional level is Windows Server 2012 R2. The forest contains the domains shown in the following table. You create a user named Admin1. You need to ensure that Admin1 can add a new domain controller that runs Windows Server 2022 to the east.contoso.com domain. The solution must follow the principle of least privilege. To which groups should you add Admin1? - 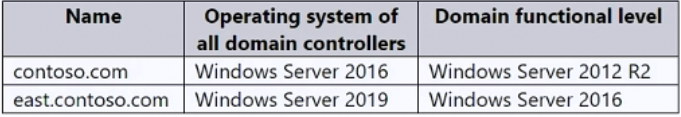
Community Votes
100% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
This question tests knowledge of AD DS promotion prerequisites and group privileges, with the common trap being the unnecessary assumption that Enterprise or Schema Admin rights are always required for newer Windows Server versions.
Adding a new domain controller requires understanding AD DS group permissions and functional level requirements. The community consensus confirms that for a Windows Server 2012 R2 forest, only local Domain Admins are needed, adhering strictly to the principle of least privilege.
Option D is frequently chosen because candidates mistakenly believe that deploying a newer Windows Server version always requires running adprep, which would demand both Enterprise Admin and Schema Admin privileges. However, since the forest functional level is already 2012 R2 or higher, no schema update is needed, making Domain Admins sufficient.
Community Discussion (6 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
When the forest functional level is Windows Server 2012 R2 or higher, Microsoft no longer requires schema extensions to introduce newer domain controllers like Windows Server 2022. Therefore, the minimum permissions needed to promote a server to a DC in a specific domain belong to that domain’s administrators. Adding Admin1 to EAST\Domain Admins provides exactly the rights required to run dcpromo locally, perfectly aligning with the principle of least privilege.Why the Other Options Are Wrong
Options B, C, and D incorrectly escalate privileges beyond what is necessary. Enterprise Admins and Schema Admins are only required when extending the AD schema or managing cross-forest operations, neither of which applies here. Granting these elevated groups violates the principle of least privilege and introduces unnecessary security risks to the forest.Community Comment Notes
Multiple verified users confirm that testing in a lab environment successfully promotes a DC using only local Domain Admins [Comment 2]. Experts clarify that legacy adprep steps were eliminated for functional levels 2008 R2 and above, directly supporting Option A [Comment 1, 4]. While one candidate questioned real-world DNS delegation needs, the exam explicitly focuses on baseline promotion permissions rather than optional configuration steps [Comment 2].Official Reference
Exam Strategy
Always check the forest and domain functional levels first; if they are 2008 R2 or higher, you can skip adprep and assume local Domain Admins are sufficient for DC promotions. Focus on the principle of least privilege by rejecting any option that includes Forest-level or Schema-level groups unless the scenario explicitly mentions schema changes or cross-domain trusts.