Which Servers Can Send Windows Firewall Logs to Microsoft Sentinel?
You have an on-premises server named Server1 that runs Windows Server 2022 Standard. You have an Azure subscription that contains the virtual machines shown in the following table. The subscription contains a Microsoft Sentinel instance named Sentinel1 in the Central US Azure region. You need to implement the Windows Firewall connector. Which servers can send Windows Firewall logs to Sentinel1? - 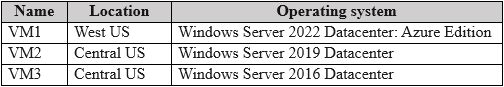
Community Votes
100% of anonymous learners picked answer E. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
The exam tests your knowledge of the Windows Firewall connector’s OS support matrix: modern Windows Server versions and on-premises servers can be connected, while the older VM3 in the table is unsupported and is the intended distractor.
This AZ-801 question tests which Windows servers can use the Microsoft Sentinel Windows Firewall connector. Based on the connector's supported operating systems and Azure Monitor Agent prerequisites, the community-validated answer is E: VM1, VM2, and Server1 only.
Choosing D (VM1, VM2, and VM3 only) is the most common error because test-takers assume all Azure VMs in the subscription are automatically supported. However, VM3 runs a legacy Windows Server version that does not meet the Azure Monitor Agent or Windows Firewall connector minimum requirements.
Community Discussion (3 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
The Windows Firewall connector for Microsoft Sentinel uses the Azure Monitor Agent (or legacy Log Analytics agent) to collect Windows Firewall events. VM1 (Windows Server 2022 Datacenter: Azure Edition) and VM2 (Windows Server 2019 Datacenter) are modern, supported operating systems, and Server1 is an on-premises Windows Server 2022 Standard machine that can also run the agent and connect to Sentinel1. Therefore these three can send logs. VM3 is excluded because it runs an older Windows Server version that is not supported by the connector.
Why the Other Options Are Wrong
Option A (VM1 only) omits VM2 and Server1, both of which are compatible. Option B (VM2 only) incorrectly omits VM1 and Server1. Option C (VM1 and Server1 only) omits VM2, which is a supported Azure VM. Option D (VM1, VM2, and VM3 only) includes VM3, but VM3 runs an unsupported legacy Windows Server version and therefore cannot send Windows Firewall logs. Option E is the only choice that includes all supported machines and excludes the unsupported VM3.
Community Comment Notes
One commenter with 5 likes pointed to the official documentation for the Log Analytics agent and Azure Monitor Agent supported operating systems, noting that support extends even to Windows Server 2012 R2, which helps clarify the boundary of the support matrix. Another highly rated comment (2 likes) explicitly explains that VM1, VM2, and Server1 are compatible with the Windows Firewall connector. A third comment asks "E or F?" because all four machines appear similar, but no F option was provided, reinforcing that E is the intended answer.
Official Reference
Exam Strategy
In the exam, identify each machine's OS version and check the data connector's support matrix before choosing. Remember that the Windows Firewall connector is not limited to Azure VMs—on-premises Windows Servers can also be monitored by installing the agent and connecting to the Sentinel workspace.