Authorizing Azure Batch Access via Service Endpoint Policy Alias
Short answer
B To Policy1, add an alias for the Azure Batch service to authorize Pool1 compute resources to access storage1 through the existing service endpoint policy.
Question
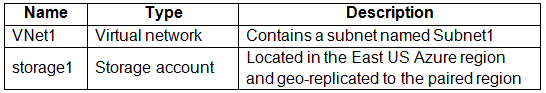
Subnet1 is associated with a service endpoint policy named Policy1. Policy1 specifies a single resource that references storage1.
To Subnet1, you deploy an Azure Batch pool named Pool1.
You need to ensure that the compute resources in Pool1 can access storage1.
What should you do?
Key Takeaways
The main trap is confusing 'Resource' (the destination) with 'Alias' (the authorized source service); since the storage account is already referenced, an alias for the Batch service must be added.
This question tests understanding of Azure Service Endpoint Policies where adding an alias is required to whitelist specific services like Azure Batch to access a storage account.
Common mistake: Users often choose 'Add a resource' (A), mistakenly believing the storage account needs to be added again, while the prompt confirms it is already referenced in Policy1.
Expert Analysis
The scenario involves Azure Service Endpoint Policies, which allow you to restrict access to a specific Azure resource (like storage1) via a service endpoint. The key constraint is that Policy1 currently references storage1 as a target resource, but the compute resources in Pool1 (deployed to Subnet1) cannot access it.
The confusion stems from the difference between a Resource and an Alias in Service Endpoint Policies:
- Resource: Specifies the target Azure service/resource being accessed (e.g., the Storage Account ID).
- Alias: Specifies the source service or workload type that is allowed to access the target resource. For example,
Microsoft.Batch/batchAccountsorMicrosoft.Compute/virtualMachineScaleSets.
In this case, storage1 is already added as a resource (the destination). However, the policy does not explicitly allow the Azure Batch service (the source) to access it. By default, service endpoints might restrict traffic to only certain known services or require explicit authorization for new workloads like Azure Batch pools.
Adding an alias for the Azure Batch service (e.g., Microsoft.Batch/batchAccounts) to Policy1 explicitly whitelists Batch pool compute nodes to reach the storage account through the service endpoint. Without this alias, the traffic may be blocked because the source identity isn't recognized as permitted by the policy.
Comments reflect this trap: some users incorrectly select 'Add a resource' (A), assuming the storage account wasn't linked, but the prompt states it is. Others correctly identify that an alias (B) is needed to authorize the specific service type (Batch) accessing the storage.
Official Reference
https://learn.microsoft.com/en-us/azure/virtual-network/manage-service-endpoints-policies
This link opens the official vendor documentation in a new tab.
Exam Strategy
When analyzing Service Endpoint Policies, always distinguish between the target resource (Resource field) and the authorized source workload (Alias field). If a resource is already listed but access fails, check if the specific service type generating the traffic has been added as an alias to the policy.
Frequently Asked Questions
What is the difference between Resource and Alias in Service Endpoint Policies?
Why didn't adding the storage account as a resource fix the issue?
Community Votes
50% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 10 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 10
-
Harish63 👍 4 Answered AB. To Policy1, add an alias: Adding an alias to Policy1 does not solve the problem because the issue is about explicitly referencing the resource, not using aliases. C. To Subnet1, add a storage endpoint for the storage service: Subnet1 already has a storage endpoint enabled (otherwise, Policy1 wouldn't work). Adding it again isn't needed. D. To Subnet1, add a subnet delegation: Subnet delegation is used to dedicate a subnet to a specific Azure service, such as Azure Batch or Azure Kubernetes Service. It does not address the issue of enabling access to the storage account.
-
manhattan 👍 2 Answered Byou can't assign nothing but Storage accounts into the service endpoint policy. you can add service/Azure/batch as Alias instead. tested in Lab, I'll go for B
-
NK203 👍 2 Answered BAssigning a service endpoint policy to a service endpoint upgrades the endpoint from regional to global scope
-
windowsmodulesinstallerworker 👍 2this is correct aliases are used to whitelist specific services to access storage accounts
-
NK203 👍 2In portal,policy definitions,resources(target),alias(source).
Show 5 more comments
-
maciek8131 👍 2 Answered AWe need resource.
-
bobothewiseman 👍 1 Answered AAdding an alias is used when referencing services using specific names (e.g., DNS names), but in this case, you need to add the actual resource (storage1) to the policy, not just an alias.
-
GohanF2 👍 1 Answered CThe answer is C. Add a storage endpoint for the storage service. Option A, which is Add a resource to Policy1, the question already specifies that storage1 is already included in Policy1
-
Sergovladi 👍 1"A" also does not work because a Resource is a target - Storage1 - which is already there. Conclusion: none of the choice
-
NK203 👍 1https://learn.microsoft.com/en-us/azure/azure-sql/managed-instance/service-endpoint-policies-configure?view=azuresql
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All AZ-700 Questions
Access 100 questions with complete answers and detailed explanations.
View Full AZ-700 Practice Test →