Update ACL Summarization for Vendor Remote Login
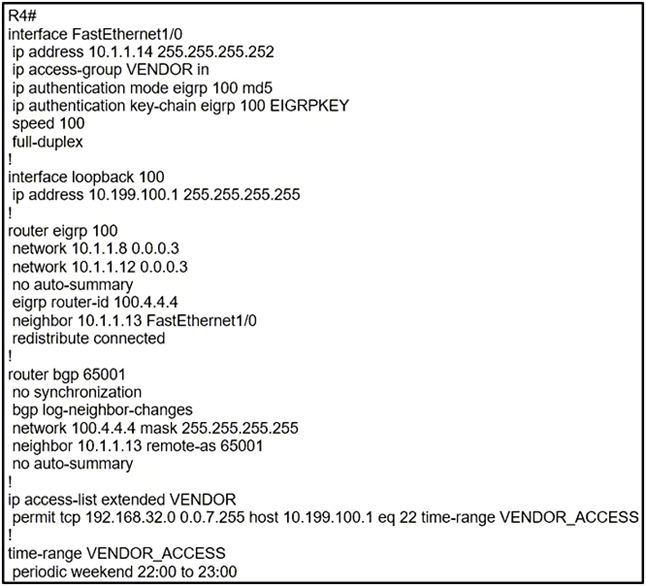 Refer to the exhibit. A network engineer received a call from the vendor for a failed attempt to remotely log in to their managed router loopback interface from 192.168.40.15. Which action must the network engineer take to resolve the issue?
Community Insight
This question tests IP access list wildcard mask calculation; the common trap is assuming the ACL covers the vendor IP or misapplying the ACL to the loopback interface instead of fixing the address range.
A vendor attempting to remotely log in from 192.168.40.15 is blocked because the VENDOR IP access list only permits the 192.168.32.0/21 range. Updating the source IP summarization in the ACL to include 192.168.40.15 resolves the access failure.
Choosing D, thinking the ACL needs to be applied to the loopback interface, which does not filter inbound VTY sessions correctly, or choosing C, assuming the loopback isn't advertised when it already is via redistribution.
Community Discussion (10 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
The IP access list VENDOR permits the 192.168.32.0 0.0.7.255 range, which covers IP addresses from 192.168.32.1 to 192.168.39.254. The vendor's source IP of 192.168.40.15 falls outside this permitted range and is implicitly denied. Updating the source IP summarization in the ACL to encompass the 192.168.40.x subnet will explicitly permit the vendor's traffic.Why the Other Options Are Wrong
Option B is incorrect because there is no indication that a time-range configuration is causing the failure. Option C is incorrect because the loopback is already advertised into EIGRP via theredistribute connected command, as noted in the community comments. Option D is incorrect because applying an inbound ACL to the loopback interface does not filter traffic destined for the router's VTY lines; access lists for remote login must be applied to the VTY lines or evaluated against the transit interface.Community Comment Notes
Commenters pointed out the ACL range limitation, with one noting the "extended access-list VENDOR: 192.168.32.0 0.0.0.7.255" does not include 192.168.40.15. Another clarified that the loopback is correctly advertised via "eigrp redistribution command", eliminating the need for a network statement. The phrasing of "source IP summarization" was questioned as awkward but technically refers to the ACL's summarized network statement.Exam Strategy
Carefully calculate the range of IP addresses covered by an ACL's network and wildcard mask. Convert the wildcard mask octets to binary to find the exact boundaries of the permitted subnet, ensuring the source IP falls within that range.
Related Analysis
Practice All 300-410 Questions
Access 159 questions with complete answers and detailed explanations.
View Full 300-410 Practice Test →