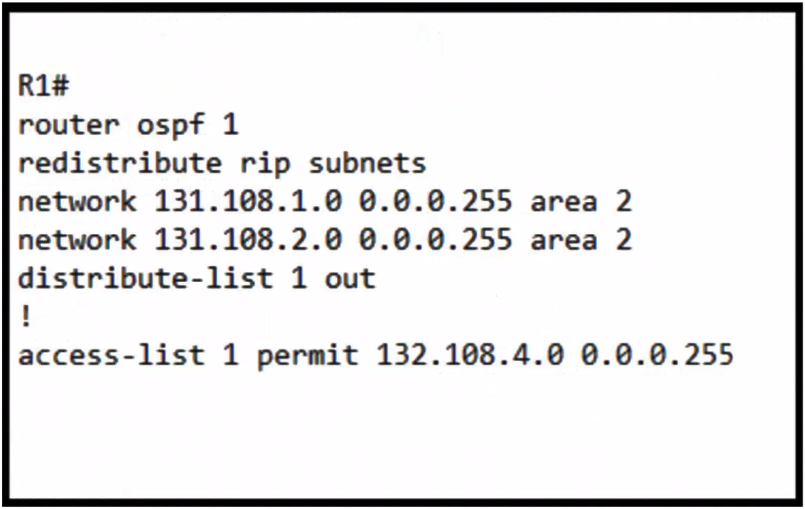
Which ACL permits OSPF type 5 LSAs for 132.108.2.0 and .3.0?
Short answer
A Access-list 1 permit 132.108.0.0 0.0.3.255 permits the range covering both 132.108.2.0/24 and 132.108.3.0/24 so their OSPF type 5 external LSAs are allowed.
Question
Key Takeaways
This item tests ACL wildcard-mask math for OSPF external LSA filtering; the trap is picking a mask that covers only 132.108.2.0/24 or the wrong 132.108.4.0 block.
R1 is missing OSPF type 5 external LSAs for 132.108.2.0/24 and 132.108.3.0/24 because the filtering ACL does not cover both prefixes. This page establishes that access-list 1 permit 132.108.0.0 0.0.3.255 (option A) is the command that permits the full 132.108.0.0–132.108.3.255 range.
Common mistake: A frequent wrong choice is D, because it permits 132.108.2.0/24 but leaves 132.108.3.0/24 filtered; C is also tempting but matches 132.108.4.0–132.108.7.255 instead.
Expert Analysis
Why the Answer Is Correct
A is correct because option A's wildcard mask 0.0.3.255 expands the ACL to cover 132.108.0.0 through 132.108.3.255, which includes both missing networks: 132.108.2.0/24 and 132.108.3.0/24. In an OSPF distribute-list scenario, the ACL must match the network addresses of the external LSAs that should be allowed; if either prefix is outside the permit range, R1 never receives its type 5 LSA. Because A includes both external subnets while no narrower or offset entry does, it is the only command that resolves the reported loss. The community consensus is unanimous on this, with alexnadal99 calling A "the only possible option."
Why the Other Options Are Wrong
Option B covers only 132.108.0.0–132.108.1.255, so neither 132.108.2.0/24 nor 132.108.3.0/24 is permitted. Option C uses 132.108.4.0 0.0.3.255, which matches the 132.108.4.0–132.108.7.255 range, the wrong side of the /22 boundary; as dancott put it, "C gives subnets.4.0 to.7.254". Option D permits exactly 132.108.2.0/24, so only one of the two type 5 LSAs is allowed and 132.108.3.0/24 remains missing. Thus B, C, and D each fail to include both advertised external networks.
Community Comment Notes
Several voters independently validated the range math. dancott and Commando1664 both noted that option C points to the.4.0–.7.255 block rather than the needed.0.0–.3.255 range. alexnadal99 described A as "the only possible option," and Chiaretta simply agreed that "A is right." Pietjeplukgeluk and Defilet also voted A, reinforcing that the community sees no ambiguity here.
Official Reference
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/iproute_ospf/command/iro-cr-book.html
This link opens the official vendor documentation in a new tab.
Exam Strategy
For ACL filtering questions, immediately translate the wildcard mask into a first-and-last address range before comparing options. Here only 0.0.3.255 covers both 132.108.2.0/24 and 132.108.3.0/24, while 0.0.0.255 covers just one of them.
Frequently Asked Questions
Why does access-list 1 permit 132.108.2.0 0.0.0.255 not solve the issue?
How does wildcard 0.0.3.255 cover both 132.108.2.0 and 132.108.3.0?
Community Votes
100% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 6 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 6
-
dancott 👍 5 Answered Ashould be A C gives subnets .4.0 to .7.254
-
alexnadal99 👍 4 Answered AIt should be A. It is the only possible option. 132.108.0.0 --- 132.108.3.255
-
Commando1664 👍 3 Answered AC gives 132.108.4.0-132.108.7.255 Should be A 132.108.0.0-132.108.4.255
-
Defilet 👍 4 Answered ASelect A as well.
-
Chiaretta 👍 3 Answered AA is right
Show 1 more comment
-
Pietjeplukgeluk 👍 2 Answered Avote a
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All 300-410 Questions
Access 159 questions with complete answers and detailed explanations.
View Full 300-410 Practice Test →