Identifying Microsoft Sentinel as a SIEM Solution
Short answer
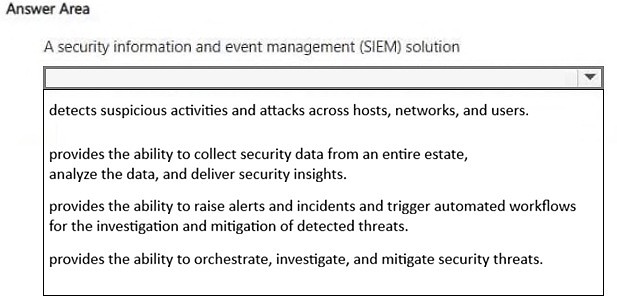
Microsoft Sentinel is the correct answer. It is the cloud-native SIEM solution designed to collect and analyze log data across an organization's digital network.
Question
Select the answer that correctly completes the sentence.
Key Takeaways
The question tests knowledge of Microsoft security service definitions, with the common trap being confusion between Sentinel (SIEM/SOAR) and Defender XDR (endpoint/cloud protection).
This SC-900 hotspot question tests the ability to identify Microsoft Sentinel as a Security Information and Event Management (SIEM) solution. The page establishes that Sentinel is the correct answer based on its core function of collecting and analyzing log data.
Common mistake: Learners often select Microsoft Defender XDR because it also handles threats, but they fail to recognize that the specific definition of 'collecting and analyzing log data' from across the network describes a SIEM, which is the primary domain of Sentinel.
Expert Analysis
Why the Answer Is Correct
Microsoft Sentinel is explicitly defined as a cloud-native Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) solution. It functions by ingesting massive volumes of log data from various sources to detect, investigate, and respond to cyberthreats in real time. This matches the description in the exhibit perfectly.
Why Other Candidate Answers Are Wrong
Other Microsoft security services like Defender for Endpoint or Purview serve different purposes. Defender focuses on endpoint and application protection rather than central log aggregation. Purview is focused on compliance and data governance. Service Trust Portal provides audit reports, not real-time threat analysis. Therefore, only Sentinel fits the SIEM definition provided.
Community Comment Notes
Community feedback strongly supports this classification. As user blh_ noted, "A SIEM (Security Information and Event Management) collects and analyzes log data... to detect, investigate, and respond to cyberthreats." This confirms the standard industry definition aligns with Microsoft's positioning of Sentinel.
Exam Strategy
Memorize the core definitions of Microsoft's security portfolio. Specifically, associate 'SIEM' and 'log analysis' with Microsoft Sentinel, and 'endpoint protection' with Microsoft Defender.
Frequently Asked Questions
What is the difference between Microsoft Sentinel and Defender XDR?
Does Microsoft Sentinel replace antivirus software?
Discussion 1 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 1
-
blh_ 👍 1COrrect. A SIEM (Security Information and Event Management) collects and analyzes log data from across an organization’s entire digital network to detect, investigate, and respond to cyberthreats in real time.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All SC-900 Questions
Access 141 questions with complete answers and detailed explanations.
View Full SC-900 Practice Test →