How Should storage2 Encrypt Azure Table Data with Fabrikam-Managed Keys?
Overview
Fabrikam, Inc. is a consulting company. The company has a main office in New York City and branch offices in Amsterdam and Singapore.
Existing Environment. Network environment
The on-premises network contains a datacenter in each office.
Existing Environment. Cloud environment
Fabrikam has two Azure subscriptions named Sub1 and Sub2 and a Microsoft 365 subscription that includes Microsoft 365 E5 licenses.
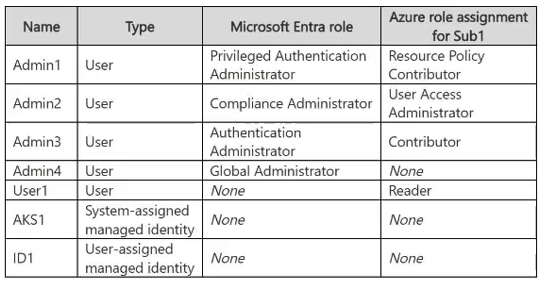
All the subscriptions are linked to a Microsoft Entra tenant named fabrikam.com that contains the identities shown in the following table.
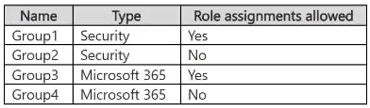
 The tenant contains the groups shown in the following table.
 All devices are enrolled in Microsoft Intune.
Existing Environment. Sub1 Resources
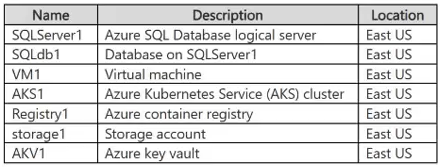
Sub1 contains a resource group named RG1 that contains the resources shown in the following table.
 SQLServer1 uses Microsoft SQL Server authentication.
Sub1 has an Azure Web Application Firewall (WAF) named WAF1 that has the following types of rule sets:
Bot Manager 1.1
Azure-managed Default Rule Set (DRS)
Sub1 has the following compliance standards assigned in Microsoft Defender for Cloud:
NIST SP 800-53 Rev. 4
Microsoft cloud security benchmark (MCSB)
System and Organization Controls (SOC) 2 Type 2
Existing Environment. Sub2 Resources
Sub2 contains a resource group named RG2.
Planned Changes and Requirements. Planned Changes
Fabrikam plans to implement the following changes:
Deploy the following key vaults to RG1:
AKV2 in the West Europe Azure region
AKV3 in the Central US Azure region
AKV4 in the East US Azure region
Deploy the following key vaults to RG2:
AKV5 in the East US region
Configure VM1 to read data from storage1.
Create function apps that have the following hosting plans:
Fa1: Flex Consumption hosting plan
Fa2: Consumption hosting plan
Fa3: Dedicated hosting plan
For WAF1, implement rate limiting rules based on the request location.
Enable the NIST SP 800-53 Rev. 5 compliance standard in Defender for Cloud.
Create a new storage account named storage2 that supports Azure Table storage.
Enforce multifactor authentication (MFA) when database administrators access SQLdb1.
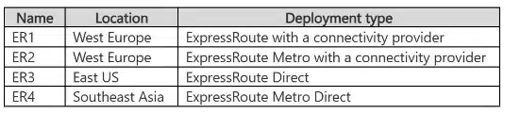
Implement ExpressRoute circuits to the on-premises network as shown in the following table.
 For RG1, create a new Privileged Identity Management (PIM) eligible role assignment that assigns the Contributor role to supported groups.
Planned Changes and Requirements. Technical Requirements
Fabrikam has the following technical requirements:
If VM1 is deleted, the permissions for VM1 must be removed automatically.
The AKS1 managed identity must only be able to pull images from Registry1.
The ID1 managed identity must be able to push images to and pull images from Registry1.
All the data in the storage accounts must be encrypted by using Fabrikam-managed keys.
All outbound traffic from the function apps to the on-premises network must use ExpressRoute circuits.
ExpressRoute connectivity between the on-premises network and the Azure environment must be encrypted by using Layer 2 or Layer 3 encryption.
You need to implement the planned change for storage2. The solution must meet the technical requirements for storage encryption.
What should you do?
Community Insight
The question tests whether you know that encryption scopes are limited to Blob containers and Azure Files, so a Table storage account must use the account-level customer-managed key instead.
Azure Table storage requires account-level customer-managed key encryption, while encryption scopes do not cover table data. The page establishes that configuring storage2's account encryption key with Fabrikam-managed keys is the correct implementation.
Choosing to create an encryption scope in storage2 because it sounds like the granular customer-managed key option, even though storage2 is for Azure Table storage and encryption scopes do not apply to table data.
Community Discussion (2 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
Configuring storage2 to use an account encryption key with a customer-managed key stored in Azure Key Vault meets the requirement that all data in the storage account be encrypted with Fabrikam-managed keys. Because storage2 supports Azure Table storage, the account-level key is the appropriate control: it applies to all data in the account, including tables, queues, blobs, and files. The option is not asking for granular container-level encryption; it is asking how to satisfy an account-wide encryption requirement for a Table-capable storage account. Therefore option C is the only choice that actually covers Table storage with Fabrikam-managed keys.Why the Other Options Are Wrong
Option A, enabling purge protection, only affects recovery of soft-deleted blobs and containers and has nothing to do with encryption key ownership. Option B, creating an encryption scope, is the common trap: encryption scopes let you apply a customer-managed key to individual blob containers or file shares, but they do not cover Azure Table storage. Option D, assigning an Azure RBAC role, controls who can access storage2 but does not change how data at rest is encrypted or which key encrypts it. None of these options satisfies the requirement that all storage data, including tables, be encrypted with Fabrikam-managed keys.Community Comment Notes
Eltooth selected C, but the comment's rationale emphasizes encryption scopes and mentions a planned "Scope1" inside storage2, which can mislead readers because a scope-level approach is not sufficient for Table storage. funmi007 selected B and correctly noted that Azure Storage encrypts data at rest by default with Microsoft-managed keys and that customer-managed keys can be configured through encryption scopes, but that explanation applies to blob containers and file shares rather than tables. The key community takeaway is that the word "scope" sounds more precise, yet the question's Table storage detail makes the account-level key the decisive factor.Exam Strategy
Read the storage service named in the question before choosing a granular encryption feature: Table storage is the signal that an encryption scope is not the right answer. When a requirement says all data in the storage account must use customer-managed keys, select the account-level key configuration rather than a blob- or file-scoped feature.Official Reference
Exam Strategy
Identify the storage service first: Azure Table storage rules out encryption scopes as the sole encryption control. For an account-wide customer-managed key requirement, choose the account encryption key configuration, not a blob- or file-scoped feature.
Frequently Asked Questions
Why doesn't an encryption scope meet the requirement for storage2?
Encryption scopes apply to Blob containers and Azure Files, not Azure Table storage, so table data would not be covered by the Fabrikam-managed key.
Does configuring the account encryption key still use Fabrikam-managed keys?
Yes. At the storage-account level you select customer-managed keys stored in Azure Key Vault, which makes the account encryption key Fabrikam-managed.
Related Analysis
Practice All SC-500 Questions
Access 100 questions with complete answers and detailed explanations.
View Full SC-500 Practice Test →