How to Achieve RCE on an Uploaded PHP File?
During an engagement, a penetration tester was able to upload to a server a PHP file with the following content: Which of the following commands should the penetration tester run to successfully achieve RCE? - 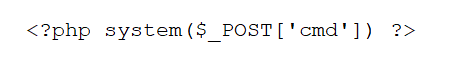
Community Votes
71% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
This question tests whether you know that the PHP shell reads POST data and that Python's requests library requires a dict, not a set, when sending form data.
For CompTIA PT0-002, the correct way to execute commands through an uploaded PHP web shell is to send a POST request with the cmd parameter; the community votes heavily for option B because it properly uses a data dictionary and reads the response with .text.
Option A is a common trap because it uses the POST method, but data={'cmd=id'} is an invalid set literal, not a dict, so the shell never receives the 'cmd' parameter.
Community Discussion (5 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
The PHP file (shown in the exhibit) likely contains code like system($_POST['cmd']);, meaning it only executes commands supplied via HTTP POST parameters. Option B sends a POST request to the shell with a properly formed dictionary {'cmd': 'id'}, and then prints the response body using .text. This satisfies both the HTTP method and the parameter naming expected by the backdoor, allowing the id command to run and return the output to the tester. Community comment [1] explicitly explains this sequence and why B achieves RCE.
Why the Other Options Are Wrong
Option A is wrong because data={'cmd=id'} is a set containing a single string, not a dictionary; running this in Python raises a TypeError when requests tries to form-encode it. Option C uses params, which sends a GET query string, but the PHP script only processes $_POST data. Option D attempts to use .test() on the response object, which does not exist; the correct attribute is .text. Comment [3] also notes that all options contain a typo in url- but this does not change the correct answer.
Community Comment Notes
The community overwhelmingly supports B (71 votes vs 29 for A). Comment [1] gives a detailed rationale: a POST request with cmd=id is required for RCE and B is the only command that does so correctly. Comment [2] shares an AI-generated explanation that reinforces the importance of the .text attribute. Comment [3] points out the universal typo and clarifies that id must be a string, which is exactly how B writes it. No credible community argument supports A; its higher vote count likely comes from hastily recognizing POST as the needed method without checking the data structure.
Official Reference
Exam Strategy
When choosing a requests command for RCE, first identify whether the server-side script expects POST or GET. Then inspect the Python syntax: data must be a dict for POST forms, and the response body is resp.text. Eliminate options with invalid methods or attributes to quickly arrive at the correct shell one-liner.