How to Enable HTTPS Access in Secure Web Proxy Rules?
Short answer
B Modify the updates-1 rule to perform the TLS inspection.
Question
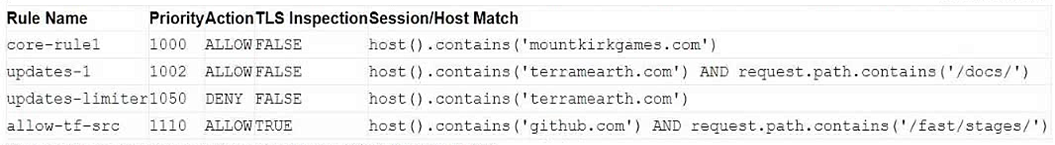
Key Takeaways
Evaluates understanding of SWP rule processing logic where HTTPS traffic bypasses rules lacking TLS inspection, commonly trapping candidates into adjusting priorities or deleting unrelated limiter rules.
This scenario tests Google Cloud Secure Web Proxy rule evaluation mechanics and the mandatory TLS inspection requirement for encrypted traffic. Community consensus confirms that enabling TLS inspection on the matching rule is the only way to allow classified HTTPS requests.
Common mistake: Option A is the most frequent wrong choice, as test-takers assume the updates-limiter rule is actively blocking the documents and incorrectly attempt to remove it instead of fixing the TLS inspection configuration.
Expert Analysis
Why the Answer Is Correct
Secure Web Proxy evaluates rules sequentially based on priority, but HTTPS traffic will only match a rule if that rule explicitly has TLS inspection enabled. Without TLS inspection enabled, the proxy skips the rule entirely and falls through to the default deny-all policy, causing access failures. Modifying the updates-1 rule to include TLS inspection allows the proxy to decrypt, classify, and apply the security policy to the requested HTTPS endpoints. This behavior ensures that only decrypted traffic can be inspected against your organization's security policies.
Why the Other Options Are Wrong
Deleting the updates-limiter rule does not resolve the issue because limiter rules typically handle bandwidth throttling or rate limiting, not access control, and they do not intercept un-inspected HTTPS traffic. Adjusting the priority of the limiter rule to 1000 merely changes its position in the rule chain without addressing the missing decryption capability. Checking Cloud NAT logs or assigning a public IP is irrelevant since Secure Web Proxy handles routing and policy enforcement independently of the VM's public IP status. These actions fail to address the root cause, which is the lack of decryption configuration on the active rule.
Community Comment Notes
Candidate [1] correctly highlights the official documentation stating that HTTPS traffic requires the TLS inspection flag to be enabled for rule evaluation. Several users initially voted for Option A due to misinterpreting the rule names, but subsequent verification confirmed that TLS inspection is the actual blocker. The consensus aligns with GCP best practices for deploying Secure Web Proxy with encrypted web traffic.
Official Reference
https://cloud.google.com/secure-web-proxy/docs/tls-rule-evaluation
This link opens the official vendor documentation in a new tab.
Exam Strategy
When troubleshooting Secure Web Proxy access issues, always verify whether the matching rule has TLS inspection enabled before adjusting priorities or removing other rules, as encrypted traffic bypasses non-decrypting policies by design.
Community Votes
67% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 3 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 3
-
Gwendal 👍 1 Answered BFor HTTPS traffic, a rule is evaluated only if it has the TLS inspection flag enabled; otherwise, that rule is skipped. https://cloud.google.com/secure-web-proxy/docs/tls-rule-evaluation#before_you_configure_tls_inspection
-
RKS_2021 👍 1 Answered AA is correct, Users will be able to access https://www.terramearth.com/docs/* without any issues,
-
1f01b87 👍 1 Answered BB is the correct answer.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All PCNE Questions
Access 80 questions with complete answers and detailed explanations.
View Full PCNE Practice Test →