Unity Catalog GRANT for Table Creation, Query, and Modify Without Grant Rights?
HOTSPOT
You have an Azure Databricks workspace that is enabled for Unity Catalog and contains a catalog named catalog1.
You have a group named group1.
You plan to create a schema named schema1 in catalog1.
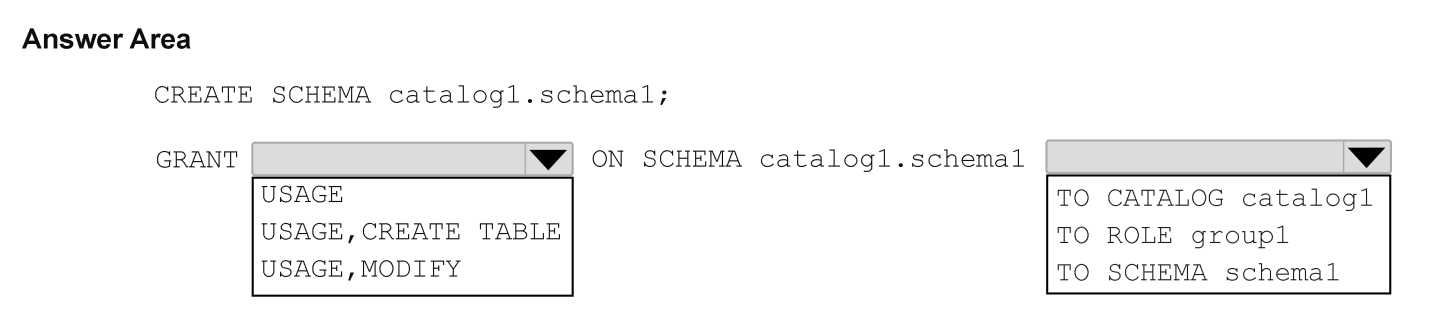
You need to ensure that group1 meets the following requirements:
Can create tables in schema1
Can modify and query tables
Cannot grant permissions for the schema and its objects
How should you complete the SQL statements? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Community Insight
Tests the minimum Unity Catalog privileges needed for DDL and DML on a schema, and the trap of granting MANAGE or ALL PRIVILEGES which would allow privilege delegation.
This DP-750 hotspot requires selecting the correct Unity Catalog privileges so group1 can create, query, and modify tables in schema1 without the ability to grant permissions. The answer grants USE CATALOG on catalog1 and USE SCHEMA, CREATE TABLE, SELECT, MODIFY on schema1, while excluding MANAGE and ownership.
A frequent error is granting ALL PRIVILEGES or MANAGE on schema1, which lets group1 grant permissions and directly violates the 'cannot grant permissions' requirement.
Community Discussion (2 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
To create tables in schema1, group1 needs CREATE TABLE on that schema. To query and modify existing tables, group1 needs SELECT and MODIFY on the schema (which cascades to all tables). Access to the catalog and schema requires USE CATALOG on catalog1 and USE SCHEMA on schema1. Crucially, the requirement to prevent group1 from granting permissions means MANAGE and ownership must be avoided, as both allow granting privileges. The correct SQL is GRANT USE CATALOG ON CATALOG catalog1 TO group1; and GRANT USE SCHEMA, CREATE TABLE, SELECT, MODIFY ON SCHEMA catalog1.schema1 TO group1.Why Other Candidate Answers Are Wrong
Granting ALL PRIVILEGES on schema1 would include MANAGE, letting group1 grant permissions, which violates the requirement. Granting only CREATE TABLE would not allow querying or modifying existing tables. Granting MANAGE or making group1 the owner of schema1 would also allow granting permissions. Using USAGE instead of USE CATALOG/USE SCHEMA is incorrect because Unity Catalog uses USE CATALOG and USE SCHEMA privileges for access.Community Comment Notes
As dgerok noted, creating tables requires "CREATE TABLE" and querying requires schema access, but their use of "USAGE" should be "USE SCHEMA" in Unity Catalog. Another commenter, zxc01, was confused because they expected to grant usage, create table, modify, and select in the first dropdown, which reflects a misunderstanding of catalog-level versus schema-level grants: the catalog only needs USE CATALOG, while the schema carries the other privileges.Official Reference
Exam Strategy
For Unity Catalog privilege questions, apply least privilege: grant only what each action requires. Remember that MANAGE and ownership enable granting privileges, so exclude them when the requirement says 'cannot grant permissions'.
Frequently Asked Questions
Why can't I grant ALL PRIVILEGES on schema1 to group1?
ALL PRIVILEGES includes MANAGE, which allows group1 to grant permissions, violating the 'cannot grant permissions' requirement.
Does group1 need USE CATALOG on catalog1 to create tables in schema1?
Yes, USE CATALOG on catalog1 is required to access the catalog before using schema1 and creating tables.