Which Azure Firewall Rule Type Filters by FQDN?
Short answer
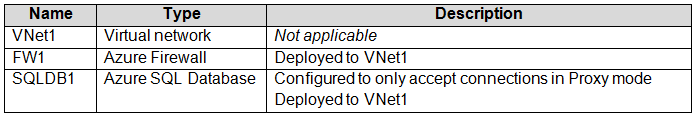
C Use an application rule on FW1 to filter traffic targeting the FQDN of SQLDB1.
Question
Key Takeaways
Azure Firewall application rules enable FQDN-based filtering, whereas network rules only support IP address-based filtering.
Azure Firewall uses application rules to filter outbound traffic based on Fully Qualified Domain Names (FQDNs). This page establishes why application rules are required over network rules when targeting an FQDN like an Azure SQL Database.
Common mistake: Choosing network rules (B) because they are commonly used for VNet traffic, but they cannot target FQDNs.
Expert Analysis
Why the Answer Is Correct
Application rules in Azure Firewall are specifically designed to allow or deny traffic based on Fully Qualified Domain Names (FQDNs). When the requirement specifies targeting the FQDN of SQLDB1, an application rule is the necessary configuration. This rule type processes traffic and can resolve the FQDN to its underlying IP addresses dynamically to enforce filtering.Why the Other Options Are Wrong
DNAT rules are used for destination network address translation, primarily to expose internal services to external traffic, not for outbound FQDN filtering. Network rules filter traffic based strictly on source and destination IP addresses, ports, and protocols, lacking the ability to resolve or target FQDNs. Infrastructure is not a valid rule type within Azure Firewall policy rule sets.Community Comment Notes
Commenters emphasized that application rules allow outbound filtering based on FQDNs, directly addressing the requirement for SQLDB1. One user noted that network rules only support IP addresses and cannot be used for FQDN targets. Another pointed out that DNAT is for inbound translation, reinforcing why application rules are the correct choice.Official Reference
https://learn.microsoft.com/en-us/azure/firewall/policy-rule-sets
This link opens the official vendor documentation in a new tab.
Exam Strategy
When an Azure Firewall question specifies filtering by FQDN, immediately look for the application rule option. Reserve network rules for IP and port-based filtering, and DNAT for inbound port forwarding.
Community Votes
100% of anonymous learners picked answer C. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 3 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 3
-
armpitworm 👍 2 Answered CSummary of the Azure Firewall rule types: A. DNAT (Destination Network Address Translation): Allows you to translate the destination IP address and port of incoming traffic to an internal IP address and port. Primarily used to expose internal services to the internet. Effectively, it maps a public IP/port to a private IP/port. B. Network Rules: Control traffic based on source and destination IP addresses, ports, and protocols (TCP, UDP, ICMP). Used for general network traffic filtering. C. Application Rules: Control traffic based on fully qualified domain names (FQDNs), HTTP/HTTPS protocols, and other application-specific attributes. Provides more granular control over web traffic. D. Infrastructure Rules: These are rules that the azure firewall uses for its own internal operations. These rules are used for things like the azure firewall reaching out to the internet for updates, or for other internal azure communications. These rules are mostly managed by Microsoft.
-
e6d6bf4 👍 2 Answered Chttps://learn.microsoft.com/en-us/azure/firewall/policy-rule-sets#:~:text=and%20any%20protocols.-,Application%20rules,-Application%20rules%20allow C is correct since the question asks to use the FW1 to filter traffic to the VNET using the FQDN of the Azure SQL. The firewall rule that support using FQDN is Application rule
-
bobothewiseman 👍 2 Answered CAzure Firewall supports Application Rules to filter outbound traffic based on FQDNs
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All AZ-700 Questions
Access 100 questions with complete answers and detailed explanations.
View Full AZ-700 Practice Test →