Minimum DCRs and DCEs for Azure Monitor Agent
Short answer
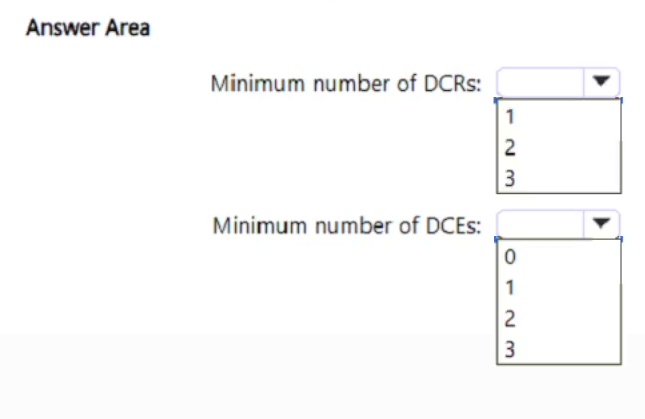
The minimum number of data collection rules required is 2, and the minimum number of data collection endpoints required is 0.
Question
HOTSPOT
You have an Azure subscription. The subscription contains a Log Analytics workspace named WS1 that is accessible via a public endpoint. The subscription contains the virtual machines shown in the following table.
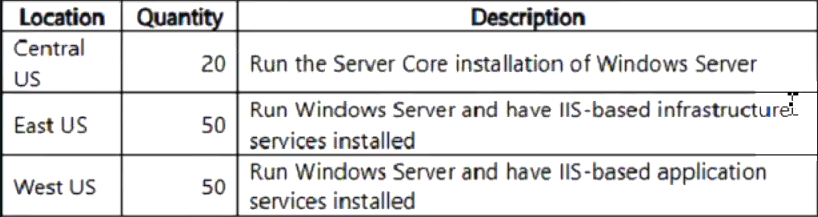 You need to collect logs from the virtual machines and forward the logs to WS1 by using the Azure Monitor Agent. The solution must meet the following requirements:
• Collect Windows logs and IIS logs from the virtual machines in the East US Azure region.
• Collect Windows logs from the virtual machines in the Central US Azure region.
• Collect IIS logs from the virtual machines in the West US Azure region.
The solution must minimize the volume of data collected.
What is the minimum number of data collection rules (DCRs) and data collection endpoints (DCEs) required? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Key Takeaways
A single DCR applies its defined data sources uniformly to all associated resources, requiring multiple DCRs for different log combinations, while DCEs are unnecessary if the Log Analytics workspace has public network access.
This scenario determines the minimum number of Data Collection Rules (DCRs) and Data Collection Endpoints (DCEs) needed to collect specific logs from Azure VMs across different regions using the Azure Monitor Agent. It establishes that two DCRs and zero DCEs are required to meet the granular log collection requirements while minimizing data volume.
Common mistake: A common mistake is assuming one DCR per region or assuming a DCE is always required for cross-region data collection, leading to over-provisioning and failing to minimize the volume of data or endpoints.
Expert Analysis
Why the Answer Is Correct
Two Data Collection Rules (DCRs) are required because a single DCR cannot selectively apply different data sources to different VMs within its scope; one DCR must collect Windows logs (associated with East US and Central US VMs) and another must collect IIS logs (associated with East US and West US VMs). Zero Data Collection Endpoints (DCEs) are required because the target Log Analytics workspace is accessible via a public endpoint, allowing the Azure Monitor Agent to send data directly without a dedicated endpoint.Why Other Candidate Answers Are Wrong
Using one DCR would force the collection of both Windows and IIS logs from all associated VMs, violating the requirement to minimize the volume of data collected by gathering unnecessary logs. Using three DCRs (one per region) would result in redundant rule definitions for the East US VMs, which need both log types. Provisioning one or more DCEs is incorrect because DCEs are only necessary when sending data over private links or when the workspace lacks public network access.Community Comment Notes
As Turnkey noted, "I WOULD PICK Select 2 DCRs / 0 DCEs" because a DCR can be associated with multiple VMs across regions. The commenter correctly points out that "WS1 uses a public endpoint", which eliminates the need for a DCE under current documented requirements for the Azure Monitor Agent.Official Reference
Exam Strategy
When calculating DCRs, remember that a DCR's data source definitions apply uniformly to all resources in its scope; to collect different data sets from different VMs, you must use separate DCRs. For DCEs, only provision them if private links or non-public endpoints are explicitly required.
Discussion 1 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded.
From public community threads 1
-
Turnkey 👍 1I WOULD PICK Select 2 DCRs / 0 DCEs under current documented requirements East US VMs receive both rules. This avoids collecting unwanted Windows logs from West US. A DCR can be associated with multiple VMs; separate VM regions do not automatically require separate rules. Microsoft: Collect guest log data Why 0 DCEs: WS1 uses a public endpoint. Microsoft’s specific DCE requirements page says AMA uses public configuration endpoints by default and currently lists Windows Firewall logs and Prometheus metrics as data sources requiring a DCE. Neither is requested here. Microsoft: When is a DCE required? Documentation qualification: The networking article still mentions allowing DCE IP addresses for IIS configurations. That note does not explicitly make DCEs mandatory for every IIS setup, but it warrants caution. My 0-DCE assessment follows the explicit DCE requirements page, rather than a live deployment test. AMA networking note
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All AZ-305 Questions
Access 95 questions with complete answers and detailed explanations.
View Full AZ-305 Practice Test →