Identifying Uninspected Traffic Risks in SFM Reports
Short answer
B Hotspot Shield must be acted upon immediately as it is a VPN application that tunnels and encrypts traffic, leading to uninspected network use.
Question
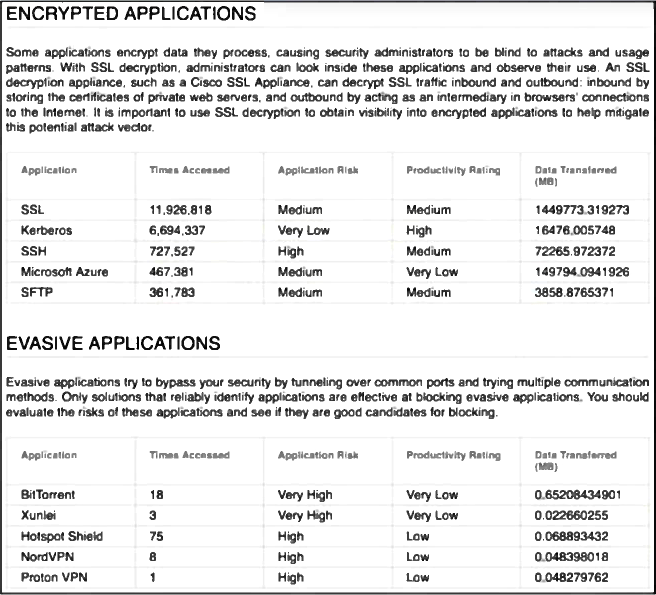
Refer to the exhibit. An engineer is analyzing a Network Risk Report generated in Cisco Secure Firewall Management Center. Against which application must immediate action be taken to prevent unauthorized and uninspected network use?
Key Takeaways
The main trap is confusing high-bandwidth applications like BitTorrent with true visibility-blind applications like VPNs; only the latter are truly 'uninspected' without TLS inspection.
Learn why Hotspot Shield is the critical threat in Cisco Secure Firewall Management Center network risk reports due to its ability to create uninspected encrypted tunnels.
Common mistake: Many candidates choose BitTorrent because it is frequently blocked for bandwidth abuse, but BitTorrent signatures are usually detected by DPI, whereas VPNs hide their payload entirely.
Expert Analysis
The core of this question hinges on the specific definition of "uninspected network use" within the context of Cisco Secure Firewall Management Center (SFM) reporting. While BitTorrent is a high-bandwidth application often blocked for policy reasons, it is typically identifiable via deep packet inspection (DPI) signatures. SSH is an encrypted protocol, but it is generally permitted or managed via certificate validation rather than being flagged as unauthorized consumer tooling.
Hotspot Shield, however, is a Virtual Private Network (VPN) application. The key trap here is distinguishing between simple encryption and tunneling. VPNs encapsulate traffic, making the payload invisible to standard firewall inspection tools unless SSL/TLS inspection is explicitly configured. In the absence of such inspection, the firewall sees only an encrypted tunnel, rendering the actual content "uninspected." This aligns directly with the risk report's warning about preventing unauthorized access that bypasses visibility controls. Comments supporting option B correctly identify Hotspot Shield as a VPN application that tunnels traffic, creating a visibility blind spot. Option D (BitTorrent) is a common distractor because it is often banned, but it is usually detectable via signature matching, not inherently "uninspected" in the same way a generic encrypted tunnel is.
Exam Strategy
When analyzing risk reports, distinguish between 'policy violations' (like P2P file sharing) and 'visibility gaps' (like unmanaged VPNs or encrypted channels). Questions asking about 'uninspected' or 'blind spot' risks almost always point to encrypted tunneling technologies rather than just high-volume traffic types.
Frequently Asked Questions
Why isn't BitTorrent the answer for 'uninspected' traffic?
How does Hotspot Shield bypass inspection?
Community Votes
50% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 2 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 2
-
Random000 👍 3 Answered DDef B, no corporate network wants BitTorrent.
-
Jackiesteele69 👍 1 Answered BHotspot Shield is a VNP application that tunnels and encrypts traffic from the endpoint making it more fitting for the "uninspected" criteria
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.