Configure Explicit Trust at the DiffServ Trust Boundary (F and G)
Short answer
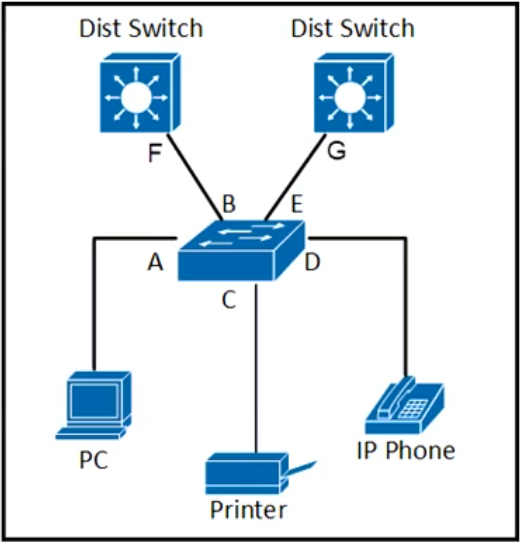
B Ports F and G are the trust boundary where access-layer traffic (already classified) enters the DiffServ domain, so explicit trust is set there.
Question
Key Takeaways
Set explicit trust at the ingress edge of the trusted domain — where marked traffic from the access layer enters (F, G). Interior/core links already carry trusted marking and do not need a new trust boundary.
Under a DiffServ model, the trust boundary is where untrusted or already-classified traffic enters the trusted QoS domain. Points F and G are the edge ports where access-layer traffic (already marked) enters, so the engineer configures explicit trust there to honor the received markings.
Common mistake: Picking A (B and E): those are deeper in the fabric where traffic is already trusted; the explicit-trust boundary is at the access edge (F, G) where markings first enter the DiffServ domain.
Expert Analysis
Why the Answer Is Correct
B is correct. F and G are the edge ports where traffic from the access layer (already classified/marked) enters the trusted DiffServ domain, so explicit trust is configured there to accept and honor the received DSCP/CoS markings.
Why the Other Options Are Wrong
A (B and E) places the trust boundary deeper in the fabric where traffic is already trusted and classified, which is not where an explicit trust boundary is needed. C (A and D) and D (C and D) are interior points, not the access-edge ingress where trust must be set.
Community Comment Notes
The vote is B (75) vs A (25). Commenters state F and G are correct because traffic is already classified by the access layer as it enters those ports.
Community Votes
75% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 3 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 3
-
TheGorn 👍 2 Answered Bhttps://networklessons.com/quality-of-service/how-to-configure-qos-trust-boundary-on-cisco-switches
-
salmarin 👍 1 Answered BF-G as traffic already classified by the access layer
-
RexChen 👍 1 Answered Ai think it's A
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All 300-420 Questions
Access 150 questions with complete answers and detailed explanations.
View Full 300-420 Practice Test →