DIA Data Policy NAT and TLOC Color Selection
An engineer modifies a data policy for DIA in VPN 200 to meet the requirements for traffic destined to these locations:
• external networks; must be translated
• external networks; must use a public TLOC color
• syslog servers, must use a private TLOC color
Here is the existing data policy configuration:
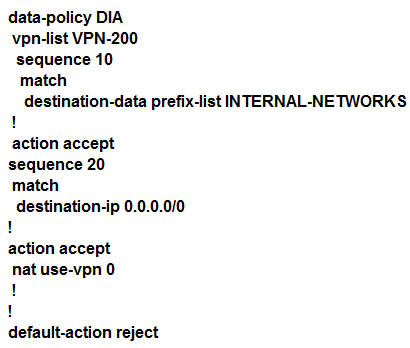 Which policy configuration sequence set meets the requirements?
Community Insight
This tests whether you can extend an existing data-policy sequence set for DIA by adding a public TLOC color to the NAT entry and steering syslog prefixes to a private color; the trap is assuming the sequences overlap or that NAT must be re-declared from scratch.
In Cisco Catalyst SD-WAN, a Direct Internet Access data policy in VPN 200 must both translate external traffic with 'nat use-vpn 0' and steer it out a public TLOC color such as biz-internet, while syslog servers are steered to a private color like mpls. The correct configuration sequence set keeps the existing NAT statement on the 0.0.0.0/0 match, adds 'set local-tloc-list color biz-internet' to that same sequence, and directs the syslog prefix list to a private TLOC color.
Many learners pick the option that splits the external-traffic requirement across two different sequence numbers or drops 'nat use-vpn 0' when adding 'set local-tloc-list color biz-internet', which would stop traffic from being translated and break DIA NAT.
Community Discussion (7 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
Option C satisfies all three requirements in one coherent edit. Sequence 20 retains the existing 'nat use-vpn 0' statement for the 0.0.0.0/0 destination match, which performs the DIA NAT translation, and augments it with 'set local-tloc-list color biz-internet' so external traffic exits over the public internet TLOC. A separate sequence matches 'destination-data-prefix-list SYSLOG-SERVERS' and sets a private TLOC color (for example mpls), keeping internal syslog traffic off the public internet path. As westh4m1234 put it, "C keeps the existing NAT use-vpno and add the color to the existing seq 20", and Daniel_666 confirms that "sequence 20 keeps existing 'nat use-vpn 0' and adds 'color biz-internet'".Why the Other Options Are Wrong
The alternatives either place the public color on a different sequence than the NAT statement, so translation and internet egress are applied to different traffic classes, or they apply the public TLOC color to the syslog match, sending syslog out the internet instead of the private transport. incog argued the reverse reading, saying "seq 20 is overlapping in option C, it seens like D is correct", but this misreads the policy: the syslog prefix list must be matched on its own sequence with a private color, not merged into the 0.0.0.0/0 NAT sequence. Removing or relocating 'nat use-vpn 0' also breaks the requirement that external networks must be translated, since NAT in DIA depends on redirecting traffic to the VPN 0 fabric. Only one option keeps NAT, a public color for external traffic, and a private color for syslog simultaneously.Community Comment Notes
The discussion converged on C, with NetArch_Teck walking through the three requirements and concluding "The nat use-vpn 0 command is for DIA Therefore the answer is option [C]". Zamochit raised the valid concern that adding a color might appear to drop NAT, but resolved it correctly by recognizing that editing sequence 20 preserves the prior 'nat use-vpn 0' statement. elninio13 asked "so we can use same sequence twice?", which points to the real subtlety: these are additive edits to existing sequences, not duplicate conflicting entries. incog's dissent in favor of D represents the minority view and does not survive the requirement that syslog use a private TLOC color.Exam Strategy
When a policy edit question shows an existing configuration exhibit, list each requirement and check that ONE sequence set satisfies all of them simultaneously rather than editing sequences independently. Never delete a functional statement like 'nat use-vpn 0' when adding an action to the same sequence.
Frequently Asked Questions
Why doesn't adding 'set local-tloc-list color biz-internet' to sequence 20 remove the NAT translation?
Editing a sequence is additive: the existing 'nat use-vpn 0' action stays in place, and the color action is added alongside it, so external traffic is still translated and exits via the public TLOC.
Why can't syslog servers use the same sequence as external networks in the DIA policy?
Syslog servers must leave over a private TLOC color, while the 0.0.0.0/0 sequence targets the public biz-internet color; matching the SYSLOG-SERVERS prefix list on its own sequence keeps the two traffic classes steered differently.
Related Analysis
Practice All 300-415 Questions
Access 120 questions with complete answers and detailed explanations.
View Full 300-415 Practice Test →