IPv6 ACL Sequence Number Troubleshooting
Short answer
D Remove the specific deny entry (sequence 30) to re-insert it earlier in the ACL order.
Question
Key Takeaways
The core test is understanding ACL processing order, where the common trap is failing to remove the existing entry before attempting to move it higher in the list.
This question tests the correct method for reordering IPv6 Access Control List (ACL) entries to enforce a deny rule before a permit rule. It establishes that removing and re-inserting specific sequence numbers is the required configuration step.
Common mistake: Learners often choose option A or C because they mistakenly target the 'permit' statement (sequence 20) instead of the 'deny' statement (sequence 30), believing they should delete the allow rule rather than reorder it.
Expert Analysis
Why the Answer Is Correct
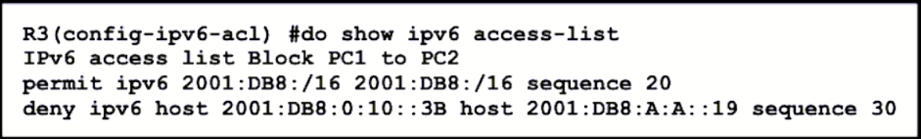
The goal is to restrict PC1 from communicating with PC2 while allowing all other traffic. In standard ACL operation, Cisco IOS processes entries sequentially from top to bottom. The exhibit implies there is already a permit any entry (likely sequence 20) which allows the traffic before a deny can take effect. To fix this, you must remove the existing sequence 30 (the specific deny rule) using no sequence 30 and then re-add it at sequence 10 so it is evaluated before the permit. Option B correctly initiates this process by deleting the misplaced deny entry.
Why the Other Options Are Wrong
Option A targets sequence 20, which is likely the 'permit any' or broader rule; deleting it would break the requirement to allow all other traffic. Options C and D contain syntax errors (config-lpv6-acl is not a valid CLI mode prompt). Therefore, only B offers the correct command syntax and logical step.
Community Comment Notes
Community consensus strongly supports B, noting that "the more specific entry should be put first." As one user noted, "You're removing sequence 30 and placing it in sequence 10," highlighting that the removal is the prerequisite for re-ordering. Another comment emphasized that "B does exactly do this" regarding keeping the existing permit intact while moving the deny up.
Exam Strategy
When troubleshooting ACLs, always check the sequence numbers and the action (permit/deny) of each line. If a broad permit exists before a specific deny, the deny is ignored. You must remove the specific entry and re-insert it at a lower sequence number.
Frequently Asked Questions
Why is 'no sequence 30' needed instead of just adding a new deny?
What happens if I delete sequence 20?
Community Votes
100% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 5 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 5
-
Coffee_bean_master 👍 3 Answered BAgree with "B." You're removing sequence 30 and placing it in sequence 10 to then deny traffic from one PC to another. Sequence 20 was allowing traffic between them.
-
Zizo_Yassin 👍 3 Answered Bthe more specific entry should be put first.
-
Pietjeplukgeluk 👍 2 Answered BB seems indeed correct, you should always keep the existing permit and move the deny above in this use case. B does exactly do this.
-
dapardo 👍 2the only one that make sense to me its B
-
d740f62 👍 1 Answered BCorrect
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All 300-410 Questions
Access 159 questions with complete answers and detailed explanations.
View Full 300-410 Practice Test →