What Vulnerability Does a Script Tag in Web Logs Indicate?
While reviewing logs, a security administrator identifies the following code: Which of the following best describes the vulnerability being exploited? - 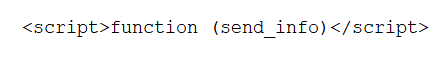
Community Votes
82% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
Candidates must recognize that injected browser-executable code points to client-side vulnerabilities, avoiding the common trap of misidentifying it as a backend database attack.
This question tests the ability to identify Cross-Site Scripting (XSS) from malicious script tags found in web server logs. The community consensus strongly confirms that client-side code injection in logs is the hallmark of an XSS attack.
SQL Injection is frequently chosen due to the shared 'injection' terminology, but SQLi payloads contain database commands (like SELECT or UNION statements), whereas the log snippet explicitly contains JavaScript execution tags meant for browsers.
Community Discussion (6 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Identifying the Attack Vector
The log snippet displays a<script> tag containing a JavaScript function. This is a definitive signature of Cross-Site Scripting (XSS). In an XSS attack, an attacker injects malicious client-side scripts into webpages viewed by other users. When the victim's browser renders this code, it executes within the trusted context of the target website.Why XSS is the Correct Answer
Option A is correct because web server logs often capture raw HTTP request bodies or URL parameters. The presence of<script> tags indicates that user input was reflected or stored without proper sanitization, allowing arbitrary JavaScript to run. As highlighted by multiple candidates in the community discussions, seeing JS functions or DOM manipulation code in logs directly correlates to XSS exploitation attempts.Eliminating Incorrect Options
- SQL Injection (B) targets relational databases using SQL syntax. Payloads typically include quotes, comments (
--,/ /), or logical operators (OR 1=1). The provided code lacks any database-specific commands, making this a distractor for those relying on keyword association rather than payload analysis. - DDoS (C) involves overwhelming a system with traffic volume, not injecting executable code snippets into application logs.
- CSRF (D) exploits authenticated sessions by tricking users into submitting unintended requests. It does not require injecting
<script>tags into the application itself; instead, it relies on social engineering and token validation flaws.
Exam Context
Security+ frequently tests payload recognition. Always analyze the syntax of the log entry: HTML/JS tags = XSS, SQL keywords = SQLi, massive concurrent connections = DDoS, and forged state-changing requests = CSRF.Official Reference
Exam Strategy
When presented with log excerpts or code snippets, immediately categorize the syntax by its intended execution environment: browser tags indicate client-side issues, while query strings or database operators point to backend vulnerabilities. Practicing payload pattern recognition will allow you to eliminate distractors rapidly and avoid overthinking purely semantic similarities.
Related Analysis
Practice All SY0-701 Questions
Access 100 questions with complete answers and detailed explanations.
View Full SY0-701 Practice Test →