What Explains Successful Password Logins Followed by Repeated MFA Failures?
Short answer
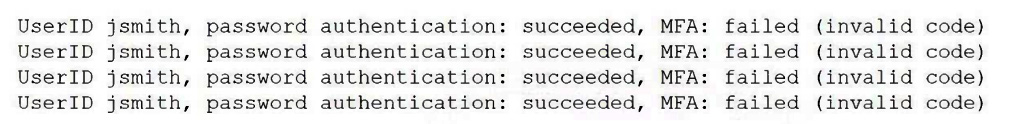
C An attacker is attempting to brute force jsmith’s account.
Question
Key Takeaways
It tests advanced log analysis by trapping candidates into choosing malware when they see valid passwords, missing that credential theft plus MFA bypass attempts is a classic modern attack vector.
This question requires interpreting authentication logs that show consistent password success paired with repeated MFA failures. The community consensus confirms this pattern indicates an attacker using compromised credentials while attempting to bypass or brute-force the second factor.
Common mistake: Candidates frequently select Option B (Keylogger) because they associate successful password entries with stolen credentials, failing to recognize that attackers routinely acquire passwords via data breaches and subsequently target MFA through repeated guessing.
Expert Analysis
Decoding the Authentication Log Pattern
The scenario presents a critical detail often missed during rushed exam conditions: multiple entries showing successful password authentication followed immediately by failed MFA authentication due to invalid codes. In modern identity frameworks, authentication is sequential. Bypassing the first factor does not grant access; the second factor must also validate successfully.
Why Option C is the Best Explanation
Option C correctly identifies an ongoing brute-force attack targeting the account. As noted by top-voted community members, attackers frequently obtain username/password pairs through dark web leaks, phishing, or credential stuffing. Once they possess the password, they proceed to the MFA stage. Since time-based or push-based MFA codes change constantly or require physical device possession, attackers resort to rapid trial-and-error (brute-forcing the MFA token) or suffer repeated rejections. This matches the exact log signature of successful first-factor authentication paired with persistent second-factor failures.
Why the Other Options Fall Short
- Option A (Account Locked Out): While repeated failures can trigger lockouts, the logs specifically highlight the pattern of success/failure rather than a terminal lockout state. Lockouts are usually a defensive outcome, not the primary attack explanation.
- Option B (Keylogger Installed): Many candidates choose this, assuming the password was stolen locally. However, as experts clarify, keyloggers explain how the password was obtained, but they do not explain the active, repetitive MFA failures observed in real-time logs. Furthermore, modern attacks rely more on cloud-based credential compromise than endpoint-specific malware for this specific log pattern.
- Option D (Ransomware Deployed): Ransomware manifests as file encryption, lateral movement, and ransom notes—not isolated authentication retry loops. There is zero correlation between the log data and ransomware indicators.
Exam Context & Community Validation
The SY0-701 exam heavily emphasizes understanding attack lifecycles and identity management controls. Community feedback consistently validates that recognizing compromised credentials coupled with MFA circumvention attempts is a core competency. As highlighted in discussions, brute-forcing isn't limited to passwords; it applies to any authentication factor, making C the only technically sound conclusion for active, repetitive guessing behavior.
Official Reference
- NIST Special Publication 800-63B: Digital Identity Guidelines
- CompTIA Security+ SY0-701 Objective 2.4: Identify characteristics and content of security reports/logs
- Microsoft Learn: Understand sign-in logs and authentication methods
These links open the official vendor documentation in a new tab.
Exam Strategy
When encountering authentication log questions, analyze the complete multi-step verification process rather than focusing solely on the initial success. If the first factor passes but the second consistently fails, prioritize answers involving compromised credentials and active bypass attempts over assumptions about endpoint malware or passive account states.
Community Votes
59% of anonymous learners picked answer C. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 25 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 25
-
nyyankee718 👍 7 Answered BCan be B or C, but leaning B Since they already have the password, its not a brute force attack
-
dbrowndiver 👍 6 Answered CThe scenario perfectly matches a common security issue where attackers gain partial access through stolen credentials but are thwarted by MFA, which they try to bypass unsuccessfully.The repeated success in password authentication suggests that the attacker has access to jsmith's password, but the failure of MFA points to an attempt to guess or brute-force the MFA code.
-
barracouto 👍 4 Answered CThe log entries show multiple successful password authentications followed by multiple failed MFA (Multi-Factor Authentication) attempts due to invalid codes. This pattern suggests that the user’s password has been correctly entered multiple times, but the MFA codes are consistently failing. The best explanation for what the security analyst has discovered is: C. An attacker is attempting to brute force jsmith’s account. The repeated successful password authentications followed by failed MFA attempts indicate that an attacker may have obtained the user’s password and is now trying to bypass the second layer of security, the MFA, by attempting multiple invalid codes.
-
leedsbarber 👍 4 Answered CBrute force involves trying different combinations of passwords/other credentials. This attacker knows the username and password and is clearly not guessing. A keylogger would know the username and password, but not have access to the MFA.
-
Etc_Shadow28000 👍 3 Answered CThe log entries indicate that the user "jsmith" has successfully authenticated with a password but has repeatedly failed the Multi-Factor Authentication (MFA) step due to an invalid code. This pattern suggests that the correct password is known or has been compromised, but the attacker is unable to provide the correct MFA code. Given this information, the most likely explanation is: C. An attacker is attempting to brute force jsmith’s account. The repeated MFA failures suggest that someone other than the legitimate user is trying to gain access, potentially indicating a brute force attempt or another form of unauthorized access where the password is known, but the second factor of authentication is not.
Show 20 more comments
-
7662357 👍 3It looks like the the password has been successfully entered, but a multi-factor authenticator is not being used correctly. If there's a keylogger installed on their computer without their knowledge they may be continuously attempting to log in to their profile to no avail. Therefore, I'd would lean more towards "B" being the correct answer.
-
c80f5c5 👍 3 Answered CIf the question mentioned a login from a specific workstation, or said its local login only, then yes it would be keylogger. However, this could be a login from home computer, mobile device, anything. Answer B could be correct but more info would be needed. Based on available info C is best.
-
Oluwasheeun 👍 3 Answered BClearly shows MFA Failed. So the most likely answer is the person knows the keys, but not the MFA. Which can be achieved by kwylogger.
-
Coznet 👍 2 Answered BB: Keylogger got the PW and is stuck on MFA. C is incorrect as MFA code changes every time so you cant brute force it. It would be possible to try the SAME code every time until you got lucky or got locked out but that aint BF.
-
e56400d 👍 2If someone enter their credentials correctly but not their MFA you can indicate that the person can be a keylogger. I think "B" is a better answer because its more specific.
-
Damique 👍 2 Answered BIt is not a brute force attack since the hacker already has the password because of the keylogger
-
123456789User 👍 2 Answered CBrute force. They have the password but are guessing the MFA code repeatedly.
-
Xavierallen9711 👍 2I’m not sure about C being correct
-
Greyhat 👍 1The correct answer is A. The user jsmith’s account has been locked out. This is because the log shows multiple failed attempts with an “invalid code” error, which is typically a result of too many incorrect password attempts. This would trigger an account lockout policy to prevent brute-force attacks. Option B. There is no indication of a keylogger in the log. Keyloggers typically don’t trigger account lockouts. Option C. While this might be a possible scenario, the log doesn’t explicitly show a brute-force attack. The “invalid code” error suggests a lockout due to incorrect password attempts, not a brute force attack. Option D. There is no indication of ransomware in the log. Ransomware typically doesn’t trigger account lockouts.
-
KSoLL 👍 1 Answered BThe answer is B. Why is it B? because If it was brute force the Password authentication would have failed and not successful. When brute force occurs, it means that the attacker is running a script to input different kind of password until it hit the right one. In this case the attacker knew the password since the password authentication successful for all four logins. And someone that say MFA failed is a brute force. yes that can be true but the right answer would be still B since the keylogger was the main issue. If MFA wasn't in place the hacker would have access to the account.
-
Aces155 👍 1 Answered CI think this is a poorly written question. A. If the user entered their MFA token incorrectly a bunch of times it possible that the system locked them out so it’s not working. B. This could be how the threat actor obtained the user’s password C. While foolish and a waste of time, attempting to guess the MFA code is essentially the same trying to guess the user’s password, thus making it a brute force attack. Given the limited information we have I’m going with C
-
shootweb 👍 1 Answered CC. It’s not B because you can brute-force anything. A brute-force attack relies on trial and error and isn’t limited to passwords—you can brute-force usernames, URLs, directories, parameters, MFA, etc. This could very well be a case of someone whose credentials (username and password) were leaked on the dark web, which also rules out B. The attacker knows the username and password but doesn’t have access to the MFA, so they are brute-forcing it.
-
SHADTECH123 👍 1 Answered CThe logs show that the password authentication for the user jsmith has succeeded multiple times, but the Multi-Factor Authentication (MFA) has failed repeatedly with an "invalid code" error. This pattern is consistent with an attacker who has obtained or guessed the user's password but is unable to bypass the MFA step, indicating a brute force attempt.
-
MAKOhunter33333333 👍 1 Answered CThis is a log of failed attempts to login (brute force), but are blocked by mfa. There is no indication of a keylogger based on this log.
-
vm_mscs 👍 1 Answered BSomeone without access to MFA successfully enters password. Password is known, how? I choose B.
-
e5c1bb5 👍 1not C. password was correct MFA was wrong. they have the password
-
Ashtom 👍 1 Answered Bin class we learned the best solution against keyloggers is MFA
-
MaxiPrince 👍 1 Answered CAn attacker is attempting to brute force jsmith’s account
-
fufuuu 👍 1 Answered BB. A keylogger is installed on jsmith’s workstation.
-
justin1995 👍 1 Answered Bthere should be invalid passwords if bruteforce
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All SY0-701 Questions
Access 100 questions with complete answers and detailed explanations.
View Full SY0-701 Practice Test →