Which Attack Uses the Same Password Across Multiple Accounts?
Short answer
A Password spraying
Question
Key Takeaways
The exam tests your ability to distinguish password spraying from brute-force: one common password against many accounts is spraying, while many passwords against one account is brute-force.
Learn how to identify password spraying from security logs. The community unanimously agrees that repeated attempts with the same password across multiple accounts indicate password spraying, not brute-force.
Common mistake: Choosing brute-force is the most common mistake, because it is a broad category; however, it involves multiple passwords per user, not the same password across many usernames.
Expert Analysis
Why the Answer Is Correct
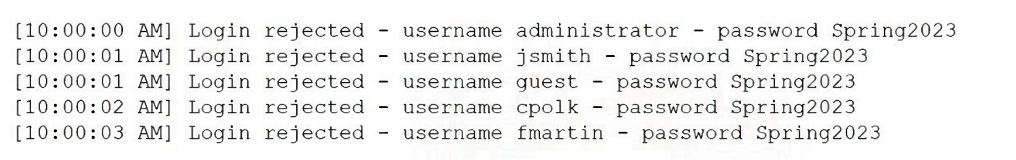
The log excerpt shows the string "Spring2023" being attempted on administrator, jsmith, guest, cpolk, and fmartin. Comment [3] notes that repeating the same password across multiple accounts strongly suggests password spraying. Comment [1] explains that password spraying systematically tries a small number of common passwords against a large number of accounts. This technique also avoids account lockouts, as noted by comment [5], because no single account receives many failed attempts.
Why the Other Options Are Wrong
- Brute-force (D) would involve many different passwords against a single account, not one password against many accounts. Comment [4] acknowledges that password spraying is a type of brute-force, but the specific pattern points to spraying.
- Pass-the-hash (C) is a credential theft technique that reuses a captured password hash, not a password guess.
- Account forgery (B) involves creating or impersonating accounts, which is not supported by the logs.
Thus, while brute-force is a related family, it does not match the exact behavior shown.
Community Comment Notes
The voting shows 100% agreement on A. Comment [5] highlights that using the same password on many accounts is a classic indication of spraying. Comment [2] simplifies the definition: using a single password to break into multiple target accounts. Comment [6] reinforces the observation: "Spring2023 was sprayed to different accounts." No authoritative comment argued for another answer.
Official Reference
- https://owasp.org/www-community/attacks/Password_Spraying
- https://www.comptia.org/certifications/security
These links open the official vendor documentation in a new tab.
Exam Strategy
Always classify the attack by the relationship between accounts and passwords. If you see one password tried on many accounts, pick password spraying; if many passwords on one account, pick brute-force. Use this distinction to eliminate wrong options quickly.
Community Votes
100% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 8 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 8
-
Luchis_69 👍 13 Answered APassword spraying is a type of brute-force attack used to gain unauthorized access to user accounts by systematically attempting a small number of commonly used passwords against many user accounts. Unlike traditional brute-force attacks, which attempt many different passwords against a single user account, password spraying involves trying a few commonly used passwords against a large number of accounts.
-
Abcd123321 👍 4 Answered APassword spraying is a cyberattack tactic that involves a hacker using a single password to try and break into multiple target accounts.
-
dbrowndiver 👍 2 Answered AThe use of the same password, Spring2023, across various accounts (administrator, jsmith, guest, cpolk, fmartin) is a classic indication of password spraying. Attackers often use this technique with passwords they expect might be used by several users, particularly common or default passwords. This Attack will avoid Account Lockouts, by trying the same password on multiple accounts rather than focusing on a single account, the attacker minimizes the risk of locking out any one user, which would alert the system to a brute-force attack.
-
habbeysax 👍 2 Answered AThe repeated use of the password "Spring2023" across multiple accounts (administrator, jsmith, guest, cpolk, fmartin) strongly suggests a password spraying attack. This method involves attempting a single, commonly used or default password across various user accounts. By distributing the attempts across multiple accounts instead of targeting just one, the attacker reduces the likelihood of triggering account lockouts. This approach allows them to avoid detection and bypass the alerts typically associated with brute-force attacks.
-
PAWarriors 👍 2 Answered ACorrect answer is A. Password Spraying is a brute force attach that tries a few common passwords against many usernames or accounts. This is effective because it avoids account lockouts and targets weak passwords.
Show 3 more comments
-
Oluwatobi4880 👍 1 Answered ASpring2023 was sprayed to different accounts
-
PukaSudu 👍 2 Answered AA. Password spraying
-
f71cbb0 👍 1 Answered ACorrect Answer: A
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All SY0-701 Questions
Access 100 questions with complete answers and detailed explanations.
View Full SY0-701 Practice Test →