Which Attack Modifies DNS Records to Redirect Services Externally?
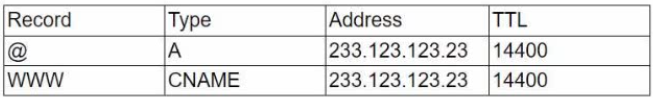
A security administrator documented the following records during an assessment of network services: Two weeks later, the administrator performed a log review and noticed the records were changed as follows: When consulting the service owner, the administrator validated that the new address was not part of the company network. Which of the following was the company most likely experiencing? - 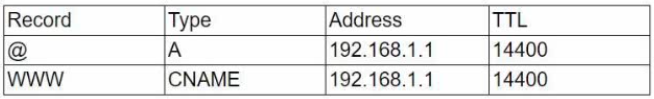 -
Community Votes
71% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
The question tests your understanding of how attackers manipulate DNS resolution tables, with the primary trap being the misattribution of redirected traffic to volumetric attacks like DDoS.
This SY0-701 practice question evaluates your ability to identify DNS poisoning based on unauthorized changes to network service records. The community consensus strongly supports DNS poisoning as the correct answer due to the explicit redirection of legitimate domain queries to external, unverified IP addresses.
Candidates frequently select DDoS attack because both scenarios involve suspicious external IP activity; however, DDoS aims to exhaust bandwidth or server capacity through massive traffic floods, whereas this scenario specifically describes the silent alteration of DNS mapping records.
Community Discussion (5 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Core Concept Identification
When a security administrator observes that documented network service records have been silently altered to point to an external IP address, the immediate indicator is DNS manipulation. DNS (Domain Name System) acts as the phonebook of the internet, translating human-readable domain names into IP addresses. When these records are modified without authorization, it typically signifies a DNS poisoning (or DNS spoofing) attack.Why DNS Poisoning is Correct
DNS poisoning occurs when an attacker injects false DNS data into a resolver's cache or modifies authoritative zone files. This causes legitimate users to be redirected to malicious servers while believing they are visiting the intended destination. In this scenario, the administrator's log review revealed changed records pointing outside the corporate network, and the service owner confirmed the new address is not company-owned. This perfectly matches the behavior of DNS poisoning, where the goal is covert traffic redirection for phishing, malware distribution, or man-in-the-middle interception.Why Other Options Are Incorrect
- DDoS attack: While DDoS involves external traffic, its primary objective is resource exhaustion through overwhelming volume. It does not inherently modify DNS records to redirect services to a specific rogue IP.
- Ransomware compromise: Ransomware focuses on encrypting data and demanding payment. Although ransomware actors may use C2 servers, the core symptom described here is record manipulation, not file encryption or system lockouts.
- Spyware infection: Spyware operates at the endpoint level to exfiltrate user data or monitor activity. It does not alter network-level DNS routing records across the infrastructure.
Community Insights & Exam Tips
As noted by multiple candidates in the discussion threads, recognizing the phrase 'records were changed' and 'address was not part of the company network' should immediately trigger DNS-related threat identification. The CompTIA Security+ exam heavily emphasizes distinguishing between availability attacks (DDoS), confidentiality/integrity attacks (DNS poisoning, MITM), and endpoint threats (ransomware, spyware). Always match the mechanism of change to the correct threat category.Official Reference
Related Analysis
Practice All SY0-701 Questions
Access 100 questions with complete answers and detailed explanations.
View Full SY0-701 Practice Test →