Azure Network Segmentation via VNets and NSGs
Short answer
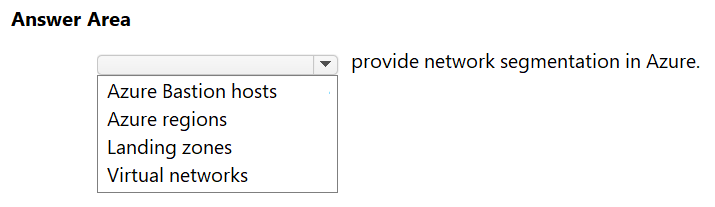
The sentence should be completed by identifying Azure Virtual Networks (VNets), subnets, Network Security Groups (NSGs), and Azure Firewall as the mechanisms providing network segmentation via software-defined boundaries.
Question
Select the answer that correctly completes the sentence.
Key Takeaways
The question tests the specific terminology for network segmentation in Azure, trapping candidates who might confuse it with physical hardware or other cloud providers' services.
This question tests your understanding of Azure infrastructure security mechanisms, specifically how network segmentation is implemented using software-defined boundaries. The correct completion identifies Azure Virtual Networks (VNets) and related tools as the primary enablers.
Common mistake: Candidates often incorrectly select options referring to physical firewalls, on-premises VLANs, or generic 'cloud security groups' that do not map directly to Azure's specific VNet/NSG architecture.
Expert Analysis
Why the Answer Is Correct
Network segmentation in Azure is achieved through software-defined boundaries rather than physical hardware. The core components include Azure Virtual Networks (VNets), which isolate resources logically; subnets, which further segment traffic within a VNet; and Network Security Groups (NSGs), which act as virtual firewalls controlling inbound and outbound traffic at the subnet or NIC level. Application Security Groups (ASGs) allow grouping VMs by application role for simpler NSG rules, while Azure Firewall provides centralized managed threat protection.
Why Other Candidate Answers Are Wrong
Incorrect options typically refer to physical networking equipment, non-Azure specific terms like 'VLANs' without context, or broader security concepts like DDoS protection which does not perform segmentation. The key distinction is that Azure relies on virtualized, software-defined networking constructs to achieve isolation and segmentation.
Community Comment Notes
Community consensus confirms that the solution involves identifying the software-defined boundary tools. As blh_ noted, "Correct. Network segmentation in Azure is provided using software-defined boundaries through Azure Virtual Networks (VNets), subnets, Network Security Groups (NSGs), Application Security Groups (ASGs), and Azure Firewall." This highlights the comprehensive list of tools involved in this capability.
Exam Strategy
When asked about network segmentation in Azure, immediately think of 'Virtual Networks' and 'Security Groups'. Distinguish between logical isolation (VNet/Subnet) and traffic filtering (NSG/Firewall).
Frequently Asked Questions
What is the difference between a VNet and an NSG?
Does Azure use physical firewalls for segmentation?
Discussion 1 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 1
-
blh_ 👍 1Correct. Network segmentation in Azure is provided using software-defined boundaries through Azure Virtual Networks (VNets), subnets, Network Security Groups (NSGs), Application Security Groups (ASGs), and Azure Firewall.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All SC-900 Questions
Access 141 questions with complete answers and detailed explanations.
View Full SC-900 Practice Test →