Analyzing Microsoft Graph API attack tactics through the MicrosoftGraphActivityLogs advanced-hunting table
Short answer
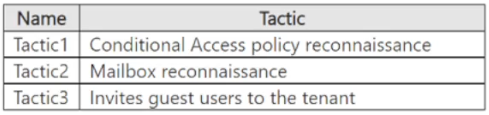
D The MicrosoftGraphActivityLogs table records all Microsoft Graph API activity, so all listed tactics are analyzable there.
Question
Key Takeaways
The MicrosoftGraphActivityLogs table in advanced hunting captures Microsoft Graph API activity across the tenant, making it the single source to investigate any tactic expressed through Graph API calls.
When an attacker uses the Microsoft Graph API as a vector, all Graph API call activity is recorded in the MicrosoftGraphActivityLogs table, so every tactic that manifests as Graph calls can be analyzed there.
Common mistake: Assuming only one tactic is visible — because the table logs all Graph API activity, any tactic carried out via Graph calls (not just one) is analyzable there.
Expert Analysis
Why the Answer Is Correct
Microsoft Defender XDR advanced hunting provides the MicrosoftGraphActivityLogs table, which records Microsoft Graph API activity in the tenant. Any attacker tactic executed through the Graph API is captured there, so all listed tactics that are expressed as Graph calls can be analyzed using this table.
Why the Other Options Are Wrong
Selecting only Tactic2 (A) or subsets (B, C) undercounts the coverage; the table logs all Graph API activity, so all tactics performed via Graph are analyzable, not just one or two.
Community Comment Notes
The community favors D (all three, 100 votes). Avaris and Vokuhila note all three can be analyzed via the table, confirming the comprehensive coverage of MicrosoftGraphActivityLogs.
Official Reference
https://learn.microsoft.com/en-us/graph/microsoft-graph-activity-logs-overview
This link opens the official vendor documentation in a new tab.
Community Votes
100% of anonymous learners picked answer D. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 4 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 4
-
Avaris 👍 5 Answered Dall 3 can be used checked it with copilot
-
Vokuhila 👍 4 Answered Dall 3 can be used
-
laddu001 👍 3actic1, Tactic2, and Tactic3
-
smanzana 👍 1C is correct
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All SC-200 Questions
Access 80 questions with complete answers and detailed explanations.
View Full SC-200 Practice Test →