What should a penetration tester report after Nmap reveals RC4 ciphers?
Short answer
A Old, insecure ciphers are in use.
Question
Key Takeaways
The exam tests whether you can identify a deprecated cryptographic algorithm (RC4) in Nmap cipher scan output and correctly report it as an insecure cipher usage rather than confusing it with other TLS-related issues.
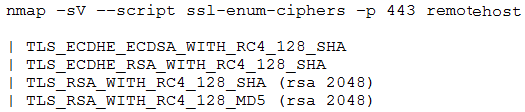
This PT0-002 question tests interpretation of Nmap ssl-enum-ciphers output, specifically recognizing that RC4-based ciphers are deprecated and insecure. Community consensus is that the correct report finding is 'Old, insecure ciphers are in use' (option A), supported by RFC 7465.
Common mistake: Choosing option B (3DES should be deprecated) or D (upgrade to TLS 1.2) – these are valid security concerns but are not directly indicated by the Nmap output, which specifically highlights RC4 usage. Candidates often overgeneralize from TLS-related findings.
Expert Analysis
Why the Answer Is Correct
The Nmap command output (not shown in the question description but implied by the image) lists several TLS cipher suites, all of which include the RC4 algorithm. RC4 is a stream cipher with known vulnerabilities, such as biased keystreams and the Bar-Mitzvah attack. Per RFC 7465, RC4 cipher suites have been deprecated and must not be used in TLS. Therefore, the correct report finding is that old, insecure ciphers are in use.
Why the Other Options Are Wrong
Option B mentions 3DES, but the output focuses on RC4, and while 3DES is also weak, it is not the primary finding. Option C refers to 2,048-bit symmetric keys, which is nonsensical (2,048-bit keys are typically RSA, not symmetric), and there is no MD5 incompatibility shown. Option D recommends upgrading to TLS 1.2, but the output does not indicate the TLS version; the issue is the cipher suite selection, not the protocol version.
Community Comment Notes
Commenter 1 explains that all listed ciphers include RC4 and that RC4 has known vulnerabilities, making A the clear choice. Commenter 2 provides a supporting reference to RFC 7465, which formalizes RC4 deprecation. Commenter 3 simply agrees. These comments reinforce that the test focuses on identifying RC4 as the insecure element, not other TLS-related options.
Official Reference
These links open the official vendor documentation in a new tab.
Exam Strategy
When you see an Nmap ssl-enum-ciphers output in a question, look specifically for algorithms known to be deprecated (e.g., RC4, 3DES, DES). If RC4 is present, the safest report statement is 'old, insecure ciphers are in use' rather than recommending a specific TLS version or commenting on key lengths.
Community Votes
100% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 3 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 3
-
Etc_Shadow28000 👍 1 Answered Anmap command indicate that the server is using several ciphers, all of which include the RC4 algorithm. RC4 is considered insecure and has known vulnerabilities. Therefore, the penetration tester should include the following in the report: A. Old, insecure ciphers are in use: The use of RC4 is considered insecure due to vulnerabilities that have been discovered in the algorithm. This is the most relevant issue based on the provided results. Explanation: B. The results do not show the use of the 3DES algorithm, so this is not relevant to the provided data. C. This statement is not accurate. The issue here is not about key size incompatibility with MD5, but rather the insecurity of using RC4 and MD5 in modern cryptographic practices. D. While upgrading to a more recent version of TLS (e.g., TLS 1.2 or TLS 1.3) is generally recommended, the primary concern highlighted by the results is the use of insecure ciphers rather than the TLS version itself.
-
opem 👍 1 Answered AA. Old, insecure ciphers are in use. The RC4 cipher suite has been deprecated https://www.keysight.com/fr/en/strikes/analysis/tls/rfc7465_rc4_cipher_deprecation.xml#:~:text=As%20of%20RFC7465%2C%20the%20RC4,suites%2C%20including%20RC4%20cipher%20suites.
-
Big_Dre 👍 1 Answered AOld, insecure ciphers are in use.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.