Identifying Pre-Sync Directory Issues Using IdFix with Least Privilege
Short answer
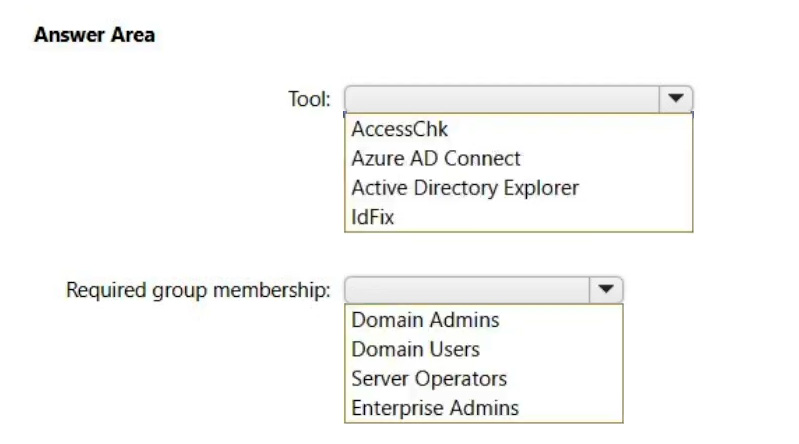
Tool: IdFix; Required group membership: Domain Users
Question
Your network contains an on-premises Active Directory domain.
You have a Microsoft 365 E5 subscription.
You plan to implement directory synchronization.
You need to identify potential synchronization issues for the domain. The solution must use the principle of least privilege.
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Key Takeaways
The trap is assuming remediation rights are needed; since IdFix is read-only, standard Domain Users permissions are sufficient and adhere to least privilege.
This page explains how to identify potential Azure AD sync issues using IdFix while strictly following the principle of least privilege by assigning the Domain Users group.
Common mistake: Selecting Domain Admins or Enterprise Admins. Learners often confuse 'identifying' issues with 'fixing' them, incorrectly assuming administrative write access is required to run the diagnostic tool.
Expert Analysis
Tool Selection: IdFix
The scenario requires identifying synchronization issues in an on-premises Active Directory domain before syncing with Microsoft Entra ID. The primary tool for this purpose is IdFix. As a lightweight, read-only utility, IdFix scans the local directory for attributes that conflict with Microsoft Entra ID requirements (such as duplicate values or invalid characters). It does not modify data; it only reports errors, making it ideal for a pre-sync audit.
Principle of Least Privilege: Domain Users
The question explicitly mandates adhering to the principle of least privilege. While tools like AD Sync Health Check require higher privileges, IdFix operates strictly as a read-only query against the directory. By default, members of the Domain Users group possess sufficient permissions to read user and computer objects in Active Directory. Since the task is limited to identifying issues rather than remediating them, elevated permissions (like those held by Domain Admins or Enterprise Admins) are unnecessary and violate the least privilege constraint. Selecting a more privileged role would be incorrect because it grants access beyond what is needed for the specific task.
Conclusion
To satisfy both the functional requirement (identifying sync issues) and the security constraint (least privilege), you must select IdFix as the tool and Domain Users as the required group membership.
Exam Strategy
Always scrutinize verbs like 'identify', 'review', or 'audit' versus 'fix', 'modify', or 'deploy'. When the task is passive or read-only, default to the lowest permission set that allows reading the target objects, typically Domain Users in AD scenarios, unless the tool documentation explicitly demands otherwise.
Frequently Asked Questions
Why can't I use Domain Admins for IdFix?
Does IdFix modify Active Directory objects?
Discussion 17 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 17
-
osxzvkwpfcfxobqjby 👍 52IdFix & Domain Users You only need to identify problems, so no rights needed to fix them. https://microsoft.github.io/idfix/Step%201%20-%20Review%20the%20prerequisites/#permissions
-
Casticod 👍 10IdFix Domain Users The application runs in the context of the authenticated user, which means that it will query the authenticated forest and must have rights to read the directory.
-
mikl 👍 6Agree - keyword here is identify!
-
vercracked_007 👍 4This must be domain admin and IDFix. A account needs read and write permissions to the domain.
-
Tomtom11 👍 3Regular" users who have accounts in an Active Directory domain are, by default, able to read much of what is stored in the directory, but are able to change only a very limited set of data in the directory. https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/plan/security-best-practices/appendix-b--privileged-accounts-and-groups-in-active-directory
Show 12 more comments
-
Amir1909 👍 2- IdFix - Domain Users
-
Tidi 👍 2lare confuser
-
Major83 👍 1Idfix and Enterprise Admins Why: Among the four roles you listed — Domain Admins, Domain Users, Server Operators, and Enterprise Admins — the most appropriate role for using IdFix, while ensuring it works properly, is: ✅ Enterprise Admins Here's a breakdown: Domain Users > Can't use iDFix Server Operators > Can't use iDFix Domain Admins > can use IDfix > Has full access, but may exceed least privilege Enterprise Admins > can use IDfix > Can access all domains in a forest, suitable for large environments 🛡️ Least Privilege Consideration: While Enterprise Admins can run IdFix successfully, it's not the ideal choice if you're strictly following the principle of least privilege. The best practice would be to create a custom account with read-only permissions on the relevant Organizational Units (OUs) in Active Directory.
-
EubertT 👍 1✅ Tool: IdFix IdFix is a Microsoft tool designed to help you identify and remediate directory issues (e.g., duplicate or invalid attributes) before syncing with Azure AD. It's lightweight, read-only, and doesn't require elevated privileges for use. ✅ Required group membership: Domain Users IdFix only requires read access to Active Directory, which a member of the Domain Users group already has. This satisfies the requirement to follow the principle of least privilege — no need for elevated rights like Domain Admin or Enterprise Admin. ✅ Final Answers: Field Selection Tool IdFix Required group membership Domain Users
-
ben.diji 👍 1Tool: IdFix Required group membership: Domain Users • • To identify issues, the tool merely performs a read-only search against the directory objects. Since standard members of the Domain Users group already possess default read-only query permissions across all objects inside Active Directory, utilizing a standard user account completely satisfies the principle of least privilege without requiring administrative delegation (like Domain Admins or Enterprise Admins).
-
feaf0a7 👍 1IDFix Domain Users The question asks "you need to identify" Domain Users can read users and other objects in Active Directory. This article helped me understand how and where the permissions are, and how to deny specific users from reading other domain objects or users. https://learn.microsoft.com/en-us/archive/technet-wiki/6130.how-to-hide-objects-in-active-directory-from-specific-users
-
azagroth 👍 1IdFix & Domain Users - any authenticated user can use the tool to view but not to edit The application runs in the context of the authenticated user, which means that it will query the authenticated forest and must have rights to read the directory. If you want to apply changes to the directory, the authenticated user needs read/write permission to the desired objects.
-
rfree 👍 1Thinking IdFix and GAdministrator https://lazyadmin.nl/it/idfix/ But to use the tool your will need of course to have read and write access to the Active Directory
-
fabiomartinsnet 👍 1I m not too experienced but think question is not well built, u need EA user Just to setup entra sync maybe this is the key
-
benpatto 👍 1It can be domain users as they're considered authenticated users, which is the MINIMUM requirement to run the tool
-
Tibo49100 👍 1It says "identify" not "fix" the potentials issues so i'll go with "IdFix & Domain Users"
-
KTM_999 👍 1bathong nikhona
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All MS-102 Questions
Access 111 questions with complete answers and detailed explanations.
View Full MS-102 Practice Test →