Fabric GraphQL API: Can SqlUsers Query or Edit SalesApi?
Short answer
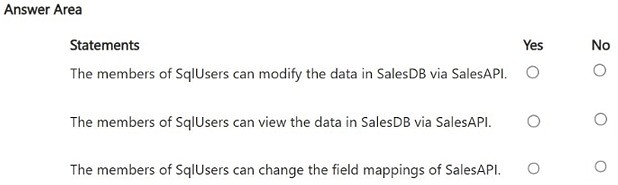
No for modifying data and No for viewing data in SalesDB through SalesApi, because Run Queries and Mutations is not granted; Yes for editing the SalesApi GraphQL item/schema.
Question
You have a Microsoft Fabric workspace named Workspace1 that contains a SQL database named SalesDB and an API for GraphQL item named SalesApi.
You have a Microsoft Entra group named SqlUsers.
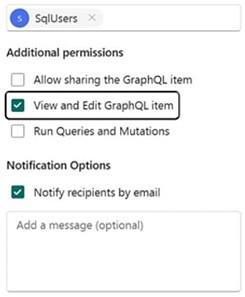
From Workspace1, you assign permission to SalesApi as shown in the following exhibit.
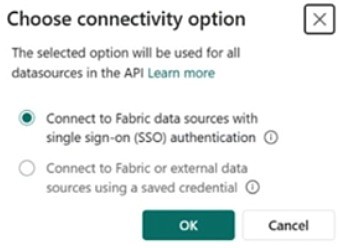
The connection to SalesDB has the connectivity option configured as shown in the following exhibit.
SqlUsers has the Viewer role for Workspace1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Key Takeaways
Tests whether you distinguish 'View and Edit GraphQL item' from 'Run Queries and Mutations'; editing the API item does not grant query or mutation execution.
Microsoft Fabric API for GraphQL authorization separates GraphQL item-edit rights from query and mutation execution. This page confirms SqlUsers can edit the SalesApi item but cannot read or modify SalesDB data through the API without Run Queries and Mutations.
Common mistake: Assuming the workspace Viewer role or the 'View and Edit GraphQL item' checkbox lets SqlUsers execute GraphQL queries or mutations; the separate Run Queries and Mutations permission is still required.
Expert Analysis
Why the Answer Is Correct
The controlling setting is the item-level permission on SalesApi: SqlUsers has "View and Edit GraphQL item" selected but not "Run Queries and Mutations". Fabric's API for GraphQL requires Run Queries and Mutations to execute any GraphQL query or mutation, so neither reading SalesDB nor modifying SalesDB data through SalesApi is possible. The separate edit permission does let the group change the GraphQL item's schema/configuration, including field mappings and relationships, so the schema-edit statement is Yes. The Workspace1 Viewer role and the SalesDB connection option do not substitute for the missing run permission. Therefore the pattern is No for data read, No for data write, Yes for GraphQL item/schema edit.
Why Other Candidate Answers Are Wrong
A Yes for viewing or modifying SalesDB data ignores the unchecked Run Queries and Mutations permission, which is mandatory for both query and mutation execution. A No for editing the SalesApi GraphQL schema confuses item-edit rights with data-execution rights; the exhibit explicitly grants View and Edit GraphQL item. The Viewer role on Workspace1 does not grant API execution because GraphQL access is governed by the API item's sharing permissions. The SalesDB connectivity option might affect which identity is used at the database layer, but it cannot overcome the missing API run permission.
Community Comment Notes
Ahmadpbi argued that the last statement should be Yes, noting that the edit permission is checked and that "This permission is independent of the Run Queries and Mutations permission." gangreja correctly separated the two data statements, explaining that modifying data is a mutation and reading data is a query, both requiring the missing Run Queries and Mutations permission. The consensus logic aligns with the Fabric permission model: edit the API definition is not the same as execute the API against SalesDB.
Official Reference
https://learn.microsoft.com/en-us/fabric/data-engineering/api-graphql-overview
This link opens the official vendor documentation in a new tab.
Exam Strategy
Find the Run Queries and Mutations checkbox first; if it is unchecked, mark every statement about reading or writing SalesDB data through SalesApi as No. Then evaluate schema/configuration statements separately against View and Edit GraphQL item.
Frequently Asked Questions
Does View and Edit GraphQL item allow SqlUsers to run queries against SalesApi?
Does the SalesDB connection option change whether SqlUsers can read data through SalesApi?
Discussion 2 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 2
-
Ahmadpbi 👍 3I think last one should be "yes". The permission View and Edit GraphQL item is explicitly checked for SqlUsers. This allows them to modify the GraphQL schema, including field mappings, relationships, and other configuration of the API item itself. This permission is independent of the Run Queries and Mutations permission.
-
gangreja 👍 1Members of SqlUsers can modify the data in SalesDB via SalesApi. No --Modifying data means running a mutation, which requires Run Queries and Mutations. That box isn’t ticked. Members of SqlUsers can view the data in SalesDB via SalesApi. No --Reading data means running a query, which needs the same missing permission, Run Queries and Mutations.“View” in “View and Edit GraphQL item” means viewing the API item itself (its definition) in the Fabric portal, not viewing the data behind it Members of SqlUsers can change the field mappings of SalesApi. Yes --Field mappings are part of the API’s definition: which tables and columns are exposed, renamed fields, and relationships. Editing them is editing the item, which is exactly what View and Edit GraphQL item grants. This item-level permission works even though the workspace role is only Viewer.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.