Read-only owner permissions on authorized_keys and open port 22 restore RSA key-based SSH access
Short answer
CD The 666 mode on authorized_keys violates StrictModes, so tighten it to owner read-only and ensure port 22 is open for the client IP.
Question
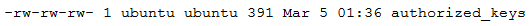
Key Takeaways
OpenSSH refuses authorized_keys files that are writable by anyone other than the owner, so the fix is removing write access, never adding execute bits.
The authorized_keys file shows -rw-rw-rw-, so group members and every other user can rewrite the file, and sshd's StrictModes rejects such permissive keys before authentication can succeed. Tightening the file so only the owner reads it and ensuring port 22 is reachable are the two actions that restore key-based access.
Common mistake: Adding execute permission to the owner (A) misreads the problem: the shown 666 mode is dangerous because of write bits, and authorized_keys is never executed, so execute rights fix nothing.
Expert Analysis
Why the Answer Is Correct
The screenshot shows authorized_keys with mode rw-rw-rw-, which means the group and all other users hold write access. OpenSSH's StrictModes check refuses to honor authorized_keys files that others can modify, so authentication silently falls back and the key pair appears broken. Removing write access so the owner has read-only control satisfies StrictModes, and confirming port 22 is open for the client's public IP restores the network path, since 22 is the default SSH port the server is stated to use.
Why the Other Options Are Wrong
A grants execute permission to the owner, but authorized_keys is a data file that sshd only reads; execute bits are irrelevant to its function and do nothing to cure the excess-write problem. B and E target port 21, which is FTP's control port and has no role in SSH connectivity, and opening port 21 to the entire internet (E) would be a security regression. D is required, but pairing it with A leaves the file still writable by others, so authentication would still fail.
Community Comment Notes
The removed-user comment cuts to the truth that authorized_keys is never executed, which undercuts option A despite its unanimous vote. PatrickH correctly dismisses every port 21 option and lands on D. FrancisDrake assumes the owner needs execute privileges and that CompTIA mainly wants the port-22 fact, but the shown mode already grants the owner read and write, so the only meaningful change is stripping the group and other write bits.
Official Reference
This link opens the official vendor documentation in a new tab.
Community Votes
100% of anonymous learners picked answer AD. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 4 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 4
-
FrancisDrake 👍 1I believe the owner needs execute privileges. Also I would assume that port 22 is open but I think CompTia wants verify that you know that the default port for SSH is port 22.
-
PatrickH 👍 1Definatly A and id also pick D over F. SSH is port 22 so any reference to Port 21 is wrong
-
[Removed] 👍 1I don't think you execute authroized_keys.
-
BlueMan93 👍 1A and D 100%
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.