Which TTP Does a SIEM Timeline of Native Utility Execution Indicate?
Short answer
D Certutil, PowerShell, bitsadmin, and rundll32 abused in the SIEM timeline are native Windows utilities, making this LOLBins use.
Question
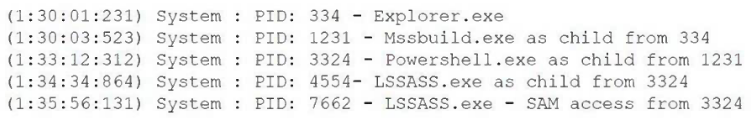
Which of the following TTPs is most likely associated with this SIEM log?
Key Takeaways
The exam tests whether you can map process-level SIEM artifacts to the correct MITRE-style TTP; the trap is picking lateral movement or credential dumping just because the server crashed.
A SIEM timeline showing certutil, PowerShell, bitsadmin, and rundll32 execution is a classic Living off the Land Binaries (LOLBins) pattern, not lateral movement or credential dumping. This page explains why option D is the best TTP match for the CA1-005 exhibit.
Common mistake: Many learners choose lateral movement (A) because PowerShell and remote-looking utilities appear, but the exhibit lacks remote logons, SMB/WMI/RDP evidence, or host-to-host authentication that lateral movement requires.
Expert Analysis
Why the Answer Is Correct
The SIEM timeline is a sequence of process-execution events, and the distinguishing artifacts are signed native Windows binaries — certutil, PowerShell, bitsadmin, and rundll32 — invoked with unusual command lines. That pattern is the definition of Living off the Land Binaries (LOLBins): attackers use trusted OS utilities for download, decoding, script execution, and payload staging while avoiding dropped malware. Certutil can fetch or base64-decode files, bitsadmin can transfer jobs, rundll32 can execute DLL exports, and PowerShell can run encoded scripts. None of those actions requires a remote logon or credential theft, so the TTP category is LOLBins use (D), not lateral movement, credential dumping, or exfiltration.
Why the Other Options Are Wrong
Lateral movement (A) would show evidence of host-to-host access, such as Type 3 or Type 10 logons, SMB/WMI/RDP/PsExec activity, or remote service creation; the exhibit's local process chain does not establish that. Credential dumping (B) would require LSASS access, a MiniDump via comsvcs.dll or procdump, Mimikatz-style behavior, or SAM/SECURITY hive export, none of which is described. Data exfiltration (C) would require outbound transfer of collected data — large uploads, rclone/FTP/HTTP POST, DNS tunneling, or cloud storage access — whereas certutil and bitsadmin here are better read as ingress or execution staging. A server crash after this activity is an outcome, not proof of A, B, or C.
Community Comment Notes
The only visible learner comment, from BWH9492, explicitly identifies the listed utilities as native OS utilities used "to run malicious scripts or download payloads" and labels them LOLBins/LOLScripts. That comment aligns with the MITRE ATT&CK and LOLBAS framing: the TTP is defined by abuse of signed system binaries, not by the crash symptom. No commenter presents evidence for lateral movement, credential dumping, or exfiltration, and the vote count is unavailable. Treat the comment as corroboration, but the decision rests on the process-level artifacts in the SIEM timeline.
Official Reference
These links open the official vendor documentation in a new tab.
Exam Strategy
When a SIEM timeline lists signed Microsoft binaries with unusual arguments, map each process to LOLBAS/MITRE ATT&CK rather than jumping to the visible outcome, such as the crash. Check whether the evidence includes remote logons for lateral movement, LSASS access for credential dumping, or large outbound transfers for exfiltration before selecting those options.
Frequently Asked Questions
Why is lateral movement wrong when the SIEM timeline shows PowerShell and certutil?
Could certutil in the SIEM log indicate data exfiltration instead of LOLBins?
Discussion 1 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 1
-
BWH9492 👍 1 Answered DNative OS utilities (certutil, powershell, bitsadmin, rundll32) executed to run malicious scripts or download payloads LOLBins (Living off the Land Binaries) LOLScripts.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.