Azure Service Endpoint Policy for Batch Storage Access
You have an Azure subscription that contains the resources shown in the following table. Subnet1 is associated with a service endpoint policy named Policy1. Policy1 specifies a single resource that references storage1. To Subnet1, you deploy an Azure Batch pool named Pool1. You need to ensure that the compute resources in Pool1 can access storage1. What should you do? - 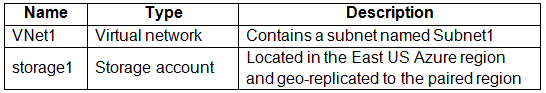
Community Votes
70% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Community Insight
The question tests the correct syntax for referencing resources in a Service Endpoint Policy, specifically distinguishing between the 'resource' property and the 'alias' property.
This page explains how to configure Azure Service Endpoint Policies to restrict access to specific storage resources. It clarifies the distinction between adding a resource and using an alias in policy definitions.
Many learners select Option B (add an alias) because they confuse the policy structure with service principal naming or assume 'alias' is the generic term for any reference. However, aliases are used for service types (like Microsoft.Storage), not specific resource instances like storage1.
Community Discussion (5 comments)
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
To ensure that compute resources in Pool1 can access storage1 via a Service Endpoint Policy (Policy1), you must explicitly add the resource 'storage1' to the policy definition. Service Endpoint Policies allow you to scope access to a specific Azure service endpoint to a single resource or a list of resources. By adding 'storage1' as a resource in Policy1, you create a whitelist that permits traffic only to that specific storage account, fulfilling the requirement.Why the Other Options Are Wrong
Option B is incorrect because an 'alias' in a Service Endpoint Policy refers to the service type (e.g., 'Microsoft.Storage'), not a specific resource instance. You cannot add a specific storage account as an alias; it must be added as a resource. Option C is redundant because Subnet1 already has the storage service endpoint enabled (implied by the existence of Policy1). Adding it again does not enforce the specific resource restriction. Option D is irrelevant; subnet delegation is used to allow specific Azure services (like App Service or Batch) to manage subnets, but it does not control access policies to other resources like storage.Community Comment Notes
Community feedback is mixed, with many users voting for B based on confusion about policy syntax. As user NK203 noted, assigning a policy upgrades scope, but this doesn't solve the specific resource reference issue. User bobothewiseman correctly points out that aliases are for service names, while Harish63 emphasizes that the issue is about explicitly referencing the resource. The majority vote for A aligns with the technical requirement to specify the target resource.Exam Strategy
When dealing with Service Endpoint Policies, always distinguish between the 'service' (alias) and the 'resource'. If the question asks to restrict access to a specific storage account, you must add the resource ID, not just enable the service endpoint.
Frequently Asked Questions
Why is adding an alias incorrect for this scenario?
An alias specifies the service type (e.g., Microsoft.Storage), not a specific resource. To target storage1, you must add it as a resource.
Does enabling the storage endpoint alone allow access?
No, enabling the endpoint allows traffic from the subnet to the service, but a Service Endpoint Policy is needed to restrict that traffic to specific resources.
Related Analysis
Practice All AZ-700 Questions
Access 100 questions with complete answers and detailed explanations.
View Full AZ-700 Practice Test →