FSLogix Profile Containers with Microsoft Entra Kerberos
Short answer
B Only User2 can implement a profile container because Microsoft Entra Kerberos authentication for Azure Files requires hybrid identities (synced from on-premises AD), whereas User1 is on-premises-only and User3 is cloud-only.
Question
You have a Microsoft Entra tenant named contoso.com that contains a user named User3 and syncs with corp.contoso.com.
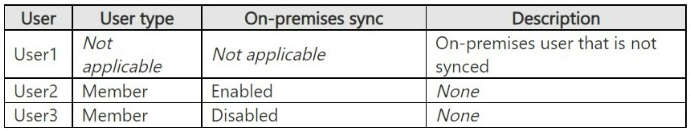
The sync status of the users is shown in the following table.
You have an Azure Virtual Desktop deployment that contains Microsoft Entra joined session hosts.
You create an Azure Storage account that has the following configurations:
• Name: storage1
• Kind: FileStorage
• File share: share1
• Microsoft Entra Kerberos: Enabled
You need to implement FSLogix profile containers on share1.
For which users can you implement a profile container?
Key Takeaways
Microsoft Entra Kerberos for Azure Files exclusively supports hybrid identities (on-prem AD synced to Entra ID); it rejects cloud-only and on-premises-only accounts.
Determine which users can access FSLogix profile containers on Azure Files when Microsoft Entra Kerberos is enabled. The solution relies on understanding that only hybrid identities are supported.
Common mistake: Candidates often select D (User2 and User3) believing that any Entra ID user can access the share because the session hosts are Entra-joined. However, Microsoft Entra Kerberos specifically excludes cloud-only identities like User3.
Expert Analysis
The core constraint in this scenario is the use of Microsoft Entra Kerberos authentication for the Azure Files share (share1). This feature allows Azure Files to authenticate users against Microsoft Entra ID without requiring network connectivity to an on-premises Active Directory Domain Services (AD DS) domain controller.
However, Microsoft Entra Kerberos has a specific identity requirement: it only supports hybrid identities. A hybrid identity is defined as a user object that exists in both on-premises AD DS and Microsoft Entra ID, with synchronization enabled from on-premises to the cloud. Cloud-only identities (created directly in Entra ID) and on-premises-only identities are not supported for this specific authentication method.
Let's evaluate the users based on their sync status:
- User1: Exists in on-premises AD but is not synced to Microsoft Entra ID. Since the user does not exist in the cloud directory, they cannot be authenticated via Microsoft Entra Kerberos. Therefore, User1 cannot access the profile container.
- User2: Is synced from on-premises AD to Microsoft Entra ID. This constitutes a hybrid identity. Even if the session hosts are Microsoft Entra joined, the storage account uses Microsoft Entra Kerberos which validates the hybrid identity. User2 is fully supported.
User3: Is a cloud-only user in Microsoft Entra ID (not synced from on-premises). The comments highlight a common misconception here. While some argue that cloud-only users might work because the hosts are Entra-joined, the documentation for Microsoft Entra Kerberos explicitly states it supports hybrid identities. It does not* support cloud-only identities for authentication against Azure Files using this specific protocol. To support cloud-only users, you would typically use Microsoft Entra ID authentication (OAuth) or SMB encryption with managed identities, but not Microsoft Entra Kerberos.
Therefore, only User2, who is a hybrid identity, can implement a profile container on share1 using Microsoft Entra Kerberos.
Official Reference
This link opens the official vendor documentation in a new tab.
Exam Strategy
When you see 'Microsoft Entra Kerberos' in an Azure Storage context, immediately filter for 'Hybrid Identity'. If the option includes cloud-only users, eliminate it. If it includes on-premises-only users without sync, eliminate it. This feature is a bridge for existing on-prem AD users, not a general Entra ID auth mechanism.
Frequently Asked Questions
Why doesn't User3 (cloud-only) work with Microsoft Entra Kerberos?
Can User1 access the share if the session hosts are Entra-joined?
Community Votes
56% of anonymous learners picked answer B. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 10 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 10
-
ViolaTriColor 👍 2 Answered BUser1 – On-prem AD only, not synced → can’t sign in to Entra-joined AVD or mount Azure Files via Entra Kerberos → no profile. User2 – Hybrid (synced) → supported User3 – Cloud-only Entra user → not supported by Entra Kerberos Microsoft Entra Kerberos authentication only supports hybrid user identities; it doesn't support cloud-only identities. https://learn.microsoft.com/en-us/azure/storage/files/storage-files-active-directory-overview
-
schpeter_091 👍 2 Answered DUsing MS Entra Kerberos, a user, such as user 3 which were syncing earlier(read the lines) but according to the question, now it's sync disabled can be configured for fslogix. The reason is, using MS Entra Kerberos does not require line of sight for a DC.
-
sojorow324 👍 2 Answered BMicrosoft Entra Kerberos authentication for Azure Files requires users to be hybrid identities, meaning they must exist in both AD DS and be synced to Entra ID with on-premises sync enabled.
-
lolo13698 👍 2 Answered DAnswer look correct. Both users 2 and 3 exists in Entra ID. User 2 is sync from on-prem AD. User 3 created directly in Entra ID.
-
Ivanvazovv 👍 1Microsoft Entra Kerberos fully supports Cloud-only identities. https://learn.microsoft.com/en-us/azure/storage/files/storage-files-identity-auth-hybrid-identities-enable?tabs=azure-portal%2Cintune
Show 5 more comments
-
kepler 👍 1 Answered DThe host pool session hosts are entra AD joined. So the cloud user can also access. On Prem AD user can access because of the sync.
-
djape 👍 1 Answered BBecause Microsoft Entra Kerberos is enabled, only users that are on-prem synced with AAD can implement FSLogix
-
Ruslan23 👍 1 Answered DDoesn't matter if User3 ha sync disabled, it still can access the profile container.
-
RabbitB 👍 1 Answered BOnly ADDS sync to Entra user can access to AVD joined ADDS domain.
-
kepler 👍 1 Answered BFSLogix only works for on prem synced users.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All AZ-140 Questions
Access 64 questions with complete answers and detailed explanations.
View Full AZ-140 Practice Test →