Enabling JIT Access for Azure Virtual Desktop Session Hosts
Short answer
D Assign a network security group (NSG) to Subnet1 to establish the required security policy boundary for all session hosts before enabling JIT access.
Question
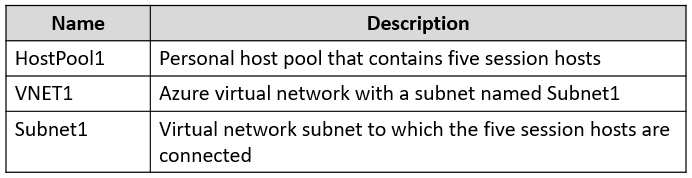
You need to enable just-in-time (JIT) VM access for all the session hosts.
What should you do first?
Key Takeaways
JIT access requires an NSG; assigning it to the Subnet is the correct first step to cover all session hosts efficiently, avoiding per-NIC configuration complexity.
Learn how to enable Just-in-Time VM access for Azure Virtual Desktop by correctly assigning an NSG to the subnet rather than individual NICs for scalable security management.
Common mistake: Choosing Option B (assigning NSGs to each NIC) is incorrect because it is operationally inefficient and violates best practices for managing multiple VMs in a shared subnet. Some candidates also mistakenly believe Azure Bastion (Option A) enables JIT, confusing two different remote access technologies.
Expert Analysis
JIT Access Prerequisites
To enable Just-in-Time (JIT) VM access via Microsoft Defender for Cloud, the virtual machines must have a Network Security Group (NSG) associated with them. The question asks what to do first to enable this feature for all session hosts. Without an NSG, there is no security policy layer for JIT to manage or modify dynamically.
Subnet vs. NIC Assignment
The core concept tested here is the scalability and best practice of NSG assignment. While NSGs can be attached to individual Network Interfaces (NICs), attaching an NSG to the Subnet is the preferred architectural pattern for managing multiple VMs within the same network segment. Attaching an NSG to Subnet1 automatically applies to all resources (session hosts) in that subnet. This avoids the operational nightmare of managing five separate NSG configurations if you were to choose Option B.
Evaluating the Options
Option A (Azure Bastion) provides secure RDP/SSH connectivity but is not the mechanism for enabling JIT access rules; it is an alternative to RDP. Option C (IAM) controls role-based access permissions, not network traffic rules. Between Options B and D, Option D is the correct first step because it establishes the necessary NSG boundary at the subnet level, covering all five session hosts efficiently. Comments highlight this debate, with some arguing for per-NIC assignment due to 'design' misconceptions, but the industry standard for AVD host pools is subnet-level security management.
Official Reference
- https://learn.microsoft.com/en-us/azure/defender-for-cloud/just-in-time-access-overview
- https://learn.microsoft.com/en-us/azure/defender-for-cloud/just-in-time-access-usage
These links open the official vendor documentation in a new tab.
Exam Strategy
When configuring security features like JIT or Azure Defender, always look for the most scalable scope first. If multiple VMs share a subnet, assign security policies (like NSGs) to the subnet rather than individual NICs. Recognize that prerequisites often involve creating the infrastructure object (the NSG) before activating the service (JIT).
Frequently Asked Questions
Why not assign NSGs to each session host NIC individually?
Does Azure Bastion replace JIT access?
Community Votes
75% of anonymous learners picked answer D. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 12 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 12
-
ZokiZokic2023 👍 3 Answered BAnswer is correct. https://learn.microsoft.com/en-us/azure/defender-for-cloud/just-in-time-access-usage
-
17Master 👍 3 Answered BCorrect, https://stefanos.cloud/kb/how-to-configure-just-in-time-jit-access-for-an-azure-vm/
-
ESAJRR 👍 3 Answered DD. Assign a network security group (NSG) to Subnet1
-
hydrillo 👍 2 Answered DAssign NSGs to each session host doesn't makes sense to a management pov.
-
Kalzonee3611 👍 2This question is absolute peak Microsoft. Anyway IMO its: D
Show 7 more comments
-
Leocan 👍 2 Answered DIt's Microsoft's suggestion.
-
jr_luciano 👍 2 Answered DCorrect answer, letter D
-
tristamm16 👍 1 Answered DThis question makes no sense, and I have a hard time believe it's on the exam. Why would you need to enable Just In Time Access for an AVD environment? Also, even if you were to enable JIT access, you wouldn't need an NSG for each session host. You would assign the same NSG to the subnet, and in turn it will apply to each host.
-
mcclane654 👍 1 Answered Dhttps://learn.microsoft.com/en-us/azure/defender-for-cloud/just-in-time-access-overview?tabs=defender-for-container-arch-aks#how-defender-for-cloud-identifies-which-vms-should-have-jit-applied Unable to test but best pratice would be to have NSG on the network. and think it should fufill this criteria
-
P4l127 👍 1By design the NSG is not deployed on subnet so if this is not stated other way B is correct since NSG is assigned to every network adapter of the VM
-
sergioandreslq 👍 1I went to Subnet and I was able to add the NSG. So, I prefer D instead B because it is more scalable. B going one-by-one is not recommended.
-
Ivanvazovv 👍 1By design there are two places where NSG can be applied - subnet and NIC.
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.
Related Analysis
Practice All AZ-140 Questions
Access 64 questions with complete answers and detailed explanations.
View Full AZ-140 Practice Test →