Configuring 802.1X Authentication Violation Replace
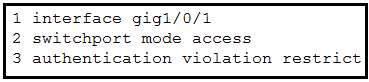 Refer to the exhibit. Network access control is implemented on the LAN and an engineer must now configure the switch port level so that users with new corporate devices can connect to the corporate LAN without issues. What must be configured next?
Community Insight
The exam tests knowledge of Cisco switch 802.1X violation modes, specifically distinguishing between standard port security violations and 802.1X authentication violations.
This question addresses configuring switch port-level settings for 802.1X network access control to ensure seamless connectivity for corporate devices. The correct configuration uses the 'authentication violation replace' command to handle authentication failures by replacing current sessions.
Candidates often select 'errdisable recovery cause psesecure-violation', confusing 802.1X authentication mechanisms with legacy port security (MAC address) configurations.
Community Discussion (5 comments)
- With the command: authentication violation replace the switch is going to remove the current session and authenticates with the new host.
Comments & Corrections
No comments yet — spotted an error or have a note? Share it below.
Expert Analysis
Why the Answer Is Correct
The correct answer is D because the scenario involves Network Access Control (NAC) using 802.1X. The exhibit shows a switch port configured withdot1x pae authenticator. When a new device connects, it must be authenticated. If an existing session is present or if the initial authentication fails but needs to be replaced to allow the new host, the authentication violation replace mode is used. This command removes the current session and attempts to authenticate with the new host, which is critical for ensuring users with new corporate devices can connect without manual intervention.Why the Other Options Are Wrong
Option A (clear port-security dynamic) is related to MAC address port security, not 802.1X authentication. Option B (shut and no shut) is a manual administrative action to reset a port, not a configuration setting for handling violations automatically. Option C (errdisable recovery cause psesecure-violation) configures automatic recovery for ports disabled due to port security violations (like MAC limit exceeded), whereas this scenario requires handling 802.1X authentication events, not generic errdisable states from port security.Community Comment Notes
Community members consistently identified D as the correct answer. As one user noted, "the command authentication violation replace the switch is going to remove the current session and authenticates with the new host." Another comment clarified that options A and C relate to port security, while the scenario explicitly mentions 802.1X, reinforcing the need for the authentication-specific violation command.Official Reference
Exam Strategy
Always distinguish between Port Security (MAC-based) and 802.1X (Identity-based) commands in NAC scenarios. Look for keywords like 'dot1x' in the exhibit to trigger the correct command set, avoiding port security specific commands like 'mac-address sticky' or 'port-security'.
Frequently Asked Questions
What is the difference between 'replace' and 'restrict' in 802.1X?
'Replace' removes the current session to authenticate the new host. 'Restrict' drops packets from unauthorized hosts while allowing authorized ones.
Why is 'errdisable recovery' incorrect here?
Errdisable recovery applies to ports disabled by safety features like port security or STP, not for managing active 802.1X authentication sessions.