Filtering a SPAN Session with a Host-Specific ACL
Short answer
A The SPAN ACL that permits only host 198.19.1.19 (wildcard 0.0.0.0) captures traffic from that single server and excludes the rest of the /24.
Question
Key Takeaways
A SPAN session uses
filter access-groupwith an IP ACL; a host wildcard (0.0.0.0) restricts the mirror to one server, while a /24 permit or subnet mask would capture the whole segment.
To mirror only traffic from server 198.19.1.19, reference a SPAN ACL that permits that host with a wildcard mask; NX-OS SPAN filtering uses wildcard masking, not subnet masks.
Common mistake: Using a subnet mask instead of a wildcard mask in the SPAN ACL, or permitting the entire 198.19.1.0/24 subnet instead of the single host the question requires.
Expert Analysis
Why the Answer Is Correct
The goal is to mirror only the traffic from server 198.19.1.19/24, not the whole subnet. A SPAN session can reference an IP ACL with filter access-group to select mirrored packets. The correct ACL permits IP from host 198.19.1.19 using a host wildcard (0.0.0.0), so only that single server's frames reach the traffic analyzer; all other addresses in 198.19.1.0/24 are excluded.
Why the Other Options Are Wrong
The other ACL variants either permit the entire 198.19.1.0/24 subnet or use an incorrect mask (subnet mask instead of wildcard), which would capture traffic from every host on the segment instead of the targeted server. A SPAN ACL must use wildcard masking, not subnet masking, on NX-OS.
Community Comment Notes
Community strongly favors A (88 votes). Racktoor notes only the /32 hostmask option isolates the single server; crooks_1988 adds that the wrong choices use a subnet mask rather than a wildcard. The differing ACL bodies live in the exhibit, but the host-only permit is the only one meeting "only from the server."
Official Reference
This link opens the official vendor documentation in a new tab.
Community Votes
100% of anonymous learners picked answer A. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 6 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 6
-
VTi 👍 3 Answered AAnswer is A. The traffic must be captured only from the server... not from entire subnet.
-
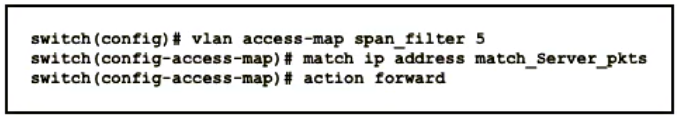
Rollizo 👍 1 Answered Ait is A Configuration Example for a SPAN ACL This example shows how to configure a SPAN ACL: switch# configure terminal switch(config)# ip access-list match_11_pkts switch(config-acl)# permit ip 11.0.0.0 0.255.255.255 any switch(config-acl)# exit switch(config)# ip access-list match_12_pkts switch(config-acl)# permit ip 12.0.0.0 0.255.255.255 any switch(config-acl)# exit switch(config)# vlan access-map span_filter 5 switch(config-access-map)# match ip address match_11_pkts switch(config-access-map)# action forward switch(config-access-map)# exit switch(config)# vlan access-map span_filter 10 switch(config-access-map)# match ip address match_12_pkts switch(config-access-map)# action forward switch(config-access-map)# exit switch(config)# monitor session 1 switch(config-erspan-src)# filter access_group span_filter
-
Racktoor 👍 1 Answered CWhat you all seem to be missing is the netmask. Only option C has a hostmask /32. Every other option has no mask or the whole subnet.
-
crooks_1988 👍 1Agree with A, also D is using a subnet mask and not a wilcard
-
timeforexam 👍 2 Answered Asuppose to be A
Show 1 more comment
-
GoForCCNP 👍 1 Answered ACorrect is A
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.