What Does the sqlmap --dbs Option Do?
Short answer
C Running sqlmap with -u and --dbs enumerates the databases in the DBMS backing the given URL.
Question
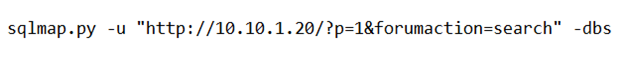
Key Takeaways
You must recognize the sqlmap tool signature (-u <url> plus --dbs) and know that --dbs is the enumeration flag that dumps database names, with the common trap being to confuse it with statement logging or exploitation options like --os-shell or --sql-shell.
The screenshot shows a sqlmap command run against a web application URL (using the -u flag) with the --dbs option, which instructs the tool to list the databases present on the back-end DBMS once an SQL injection point has been identified. This page confirms that the command's purpose is enumerating the databases in the DBMS for the given URL, not retrieving live statements or planting backdoors.
Common mistake: Option C is right, but learners often pick A or D, imagining that a captured command is streaming or searching executed SQL statements; sqlmap in this mode does not return live statement traffic, it queries DBMS metadata to list database names, while B describes post-exploitation behavior enabled by other options.
Expert Analysis
Why the Answer Is Correct
The command shown is the canonical sqlmap invocation pattern: sqlmap -u "http://…/page.php?id=1" --dbs. The -u switch supplies a full target URL, which tells sqlmap to test the parameters of that web page for injectable flaws. The --dbs switch is sqlmap's flag to enumerate all databases the DBMS exposes to the injecting account, producing a listing such as available databases: information_schema, mysql, …. This is the standard first discovery step in a SQL injection engagement, matching CEH's flow of injecting, then fingerprinting, then enumerating schema objects. That makes option C the exact description of the command's function.
Why the Other Options Are Wrong
Option A describes reading executed SQL statements, which is traffic/monitoring behaviour (e.g., a proxy or DB audit log) rather than what --dbs does; sqlmap's --sql-shell is a different option and even it runs attacker-supplied queries rather than 'retrieving' statements. Option B refers to creating backdoors, which would require heavier sqlmap options such as --os-shell, --os-cmd, or writing webshells with --file-write/--file-dest — none of which appear here. Option D wrongly reframes the target as an IP address; sqlmap was pointed at a URL, and its queries go to the web application that fronts the DBMS, not directly to an IP for 'searching statements'.
Community Comment Notes
The community is unanimous here: every recorded vote is for C, and insaniunt's comment explains the reasoning well, noting that 'It uses SQLMap, a popular tool for automated detection and exploitation of SQL injection vulnerabilities' and that '--dbs option indicating that it should enumerate the databases.' LordXander adds, more loosely, that C 'is the only one that makes sense' given the remaining distractors. One commenter expressed doubt about the reliability of the shared information, but the tool's documented behaviour settles the question independently of that uncertainty.
Official Reference
This link opens the official vendor documentation in a new tab.
Exam Strategy
On CEH 312-50v12 screenshots, first identify the tool by its flags: -u with a URL plus long-form switches is sqlmap. Then map the switch to its documented function (--dbs = list databases, --tables, --columns, --dump, --os-shell = backdoor/shell), since the distractors almost always describe a different sqlmap capability.
Frequently Asked Questions
What sqlmap options would actually create a backdoor instead?
Community Votes
100% of anonymous learners picked answer C. Votes are pick records left by other test-takers — they are not the verified answer.
Discussion 3 contributions
Compiled from public community threads and reader submissions, lightly edited for clarity. Handles and vote tallies are shown as recorded, and comments reflect the views of individual contributors.
From public community threads 3
-
insaniunt 👍 4 Answered CC. Enumerating the databases in the DBMS for the given URL It uses SQLMap, a popular tool for automated detection and exploitation of SQL injection vulnerabilities, with the --dbs option indicating that it should enumerate the databases.
-
qtygbapjpesdayazko 👍 1Im not certain about the reliability of that information
-
LordXander 👍 1 Answered CBecause is the only one that makes sense
Reader comments & corrections
No reader corrections yet — spotted an error or have a note? Share it below.